
One rule set to manage challenge everything outside Australia: (not ip.geoip.country in {"AU"}) and to be honest, you could just block everything outside Australia for a footy site such as yours.


You would think that but the second I put whole country blocks in place I had members emailing me who lived in those countries. Majority of or traffic comes from Australia however we have members in lots of south East Asian countries, all over Europe, us Canada and South America. So entire country blocks always end up dudding someone.One rule set to manage challenge everything outside Australia: (not ip.geoip.country in {"AU"}) and to be honest, you could just block everything outside Australia for a footy site such as yours.
If it does happen only occasionally it may be a glitch in the matrix: IPs get reassigned quite frequently, either from one ASN to another or to a different location within an ASN. IP geolocation is not an exact science anyway plus the free version of the maxmind db may have some delays from time to time, the more as it is downloaded only every couple of days. Also, sometimes announcements of the IP owners are bogus, missing or simply wrong - deliberately or accidentally. All of that is typically not a huge issue (and temporary anyway), but it may be the explanation of what you see.I'm seeing countries like Bangladesh and Hong Kong in the list of current guests and I have blocked them. So, how come I'm seeing them?

I don't know if it's a glitch or something else but for some reason Hong Kong and Bangladesh keep appearing in the list of visitors.If it does happen only occasionally it may be a glitch in the matrix: IPs get reassigned quite frequently, either from one ASN to another or to a different location within an ASN. IP geolocation is not an exact science anyway plus the free version of the maxmind db may have some delays from time to time, the more as it is downloaded only every couple of days. Also, sometimes announcements of the IP owners are bogus, missing or simply wrong - deliberately or accidentally. All of that is typically not a huge issue (and temporary anyway), but it may be the explanation of what you see.
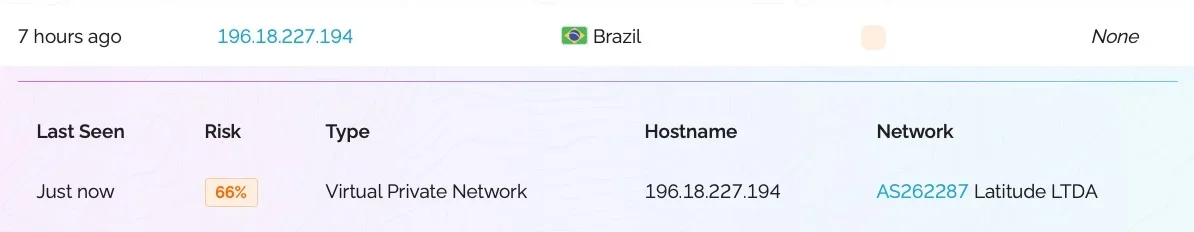
I.e. I've blocked Brazil completely, yet today I had an IP from there in my proxycheck logs (which usually is not the case due to the country blocking):
View attachment 338882

Release Notes:
...This release aims to resolve a rare race condition error that could occur during the cleanup of cache files, particularly on Windows Server and high-traffic environments. Thanks to architectural improvements, manual cache clearing operations or intensive cron tasks will no longer trigger false warnings in the Server Error Logs. As this update does not involve any database or template changes, it can be safely updated by simply overwriting the files.

No API key required for most services. Blackbox has free tiers; higher-volume access requires a RapidAPI key.
This is a critical maintenance update released to ensure our add-on operates flawlessly with the recently rolled-out XenForo 2.3.12 version.
In XenForo 2.3.12, the core developers introduced highly strict rule changes to the underlying "Class Extension (Class Proxy)" mechanism (specifically concerning stripped alias merging). These changes broke backward compatibility, causing features that worked perfectly in previous versions to suddenly trigger crashes (Fatal Errors) or silent...
This maintenance and quality-of-life update enhances the "IP Activity by Time" monitor on the admin dashboard.
In previous versions, activity distribution was aggregated based on the database server's default timezone (typically UTC). With version 1.0.33, the dashboard automatically adapts to the viewing administrator's local timezone configured in their XenForo account. Threat activities occurring throughout the day (Night, Morning, Day, Evening) are now accurately mapped to...
With this update, we are thrilled to bring one of the most requested features to life, along with an important data mapping improvement!
New Feature: Country Whitelist (Allowlist) Mode
You no longer need to manually add dozens or hundreds of countries to a block list!
With the newly introduced "Country Filter Mode", you can now switch the country filter to Whitelist Mode. In this mode, only visitors originating from your selected countries (e.g., US, Canada, UK) will be...
This update focuses on internal security hardening, administrative permission consistency, and navigation permission alignment in accordance with XenForo 2.3.x core standards. All improvements have been implemented without altering the high-performance cache-first architecture or core rate-limiting workflows.
- Security Hardening:
- Hardened the client validation check in the Rate Limit Captcha controller (
RateLimitCaptcha.php). Replaced...
We are delighted to announce the release of IP Threat Monitor 1.0.36! This update focuses heavily on real-world stability, server storage efficiency, and deep alignment with the XenForo 2.3 ecosystem based on direct feedback from our customers.
- Smart Storage & Disk Optimization:
We completely revamped the file-based caching mechanism to eliminate disk clutter and folder slowdowns. Cache files are now neatly organized into balanced subdirectories, and expired temporary...
This update focuses heavily on real-world reliability, ensuring that your community remains protected and smooth even during sudden visitor traffic spikes, while keeping your search engine presence completely safe.
What's New in Version?
- Rock-Solid Stability During Traffic Surges:
We refined our background monitoring engine to eliminate any friction or conflicts when hundreds of visitors hit your forum at the exact same moment. The protection runs...
In this version, our primary focus has been maximizing system security, preserving forum speed and server resources, achieving seamless visual compatibility with XenForo 2.3, and incorporating valuable user feedback to make administration even smoother.
Key Highlights
1. Advanced Fake Bot Protection
A strict verification mechanism has been implemented to prevent malicious actors and scrapers from bypassing rate limits by spoofing legitimate search engine...

We use essential cookies to make this site work, and optional cookies to enhance your experience.