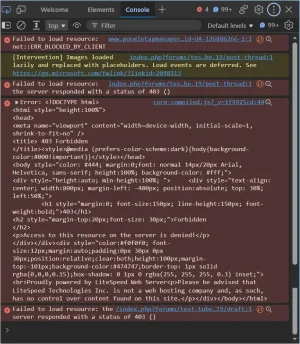
This is the response I received from my host. It's quite honestly way over my head.
We reviewed the server logs and confirmed that the 403 response is being generated by the server's ModSecurity security layer while processing the XenForo request.
The affected request was recorded as follows:
[13/Sep/2026:08:45:56 -0700]
Client IP: 143.59.217.158
Destination: 23.254.252.225:443
POST /index.php?forums/test-tube.19/draft HTTP/1.1
Host: forum.dreamcap.org
Content-Length: 1947
X-Requested-With: XMLHttpRequest
Accept: application/json
Content-Type: multipart/form-data
Origin:
https://forum.dreamcap.org
Referer:
https://forum.dreamcap.org/index.php?forums/test-tube.19/post-thread
The request was then blocked with the following ModSecurity rule:
HTTP/1.1 403 Forbidden
Rule ID: 949110
Message: Inbound Anomaly Score Exceeded (Total Score: 25)
Severity: CRITICAL
MatchedString: 25
The audit log also shows the underlying rule that contributed to the anomaly score:
Rule ID: 941100
Message: XSS Attack Detected via libinjection
File: REQUEST-941-APPLICATION-ATTACK-XSS.conf
Line: 29
Severity: CRITICAL
MatchedString: 1
This indicates that ModSecurity's XSS detection identified part of the XenForo request as a potential XSS pattern. The 949110 rule then enforced the 403 response after the request's anomaly score reached the configured threshold.
We also found another request from the same client IP that was blocked with an anomaly score of 10:
HTTP/1.1 403 Forbidden
Rule ID: 949110
Message: Inbound Anomaly Score Exceeded (Total Score: 10)
Severity: CRITICAL
MatchedString: 10
Based on these findings, the issue appears to involve the way the XenForo editor/draft request is being interpreted by the server's web application firewall. We recommend having your XenForo/website developer review the posting functionality and the request being generated when an emoji is included, as they may be able to identify why the request is triggering the XSS detection.
Since this is a shared hosting environment, we cannot disable ModSecurity globally or broadly whitelist the security rule, as this could affect the security of other customers on the server.
At this stage, we recommend having your website/XenForo developer review the affected editor/posting functionality as well, particularly how the emoji-containing content is being submitted. They may be able to determine why the request is being interpreted as an XSS pattern by the security rule.
If the developer confirms that the request is legitimate and identifies the specific request/content being flagged, please provide those details to us. We can then review whether a safe, scoped server-side adjustment is possible for the domain.