Forum Copilot: Free iOS & Android App for XenForo (Open Source)

Forum Copilot: Free iOS & Android App for XenForo (Open Source) 1.10.0

No permission to download
I briefly looked into this and believe the plugin sends the admin’s email address, along with some additional details, to the developer’s server whenever the plugin admin dashboard is accessed.

@forumcopilot , would you mind clarifying what data is transmitted? For example, are private messages also sent back to your server?

I think it’s important if not policy to disclose this.
 
I briefly looked into this and believe the plugin sends the admin’s email address, along with some additional details, to the developer’s server whenever the plugin admin dashboard is accessed.
Just to clarify, the concern here is that we were contacted unexpectedly using license-related information that was never provided to this developer directly. We never opted into, subscribed to, or requested any form of marketing communication from them in the first place.

What makes this concerning is that this individual clearly had access to certain XF license details, as well as non-public email addresses. We’ve asked multiple times where this information originated from, yet there has been no public response or clarification regarding the source of the data.

To reiterate, this does not appear to be an issue with XenForo (company) itself. Based on the circumstances, it seems far more likely that the information originated from a third-party vendor or developer that previously had access to these details and either shared or sold the data elsewhere.
 
I'm no developer, so I could be wrong, but looking at the code for this add-on it appears to me that this add-on creates a way for the developer to gain access to a forum's complete data (users, posts, DMs, etc) using their own API. Maybe that's how they got the info? It would be nice if @Chris D, or some other developer, would take a look at this add-on and determine if that would be possible.
 
I'm no developer, so I could be wrong, but looking at the code for this add-on it appears to me that this add-on creates a way for the developer to gain access to a forum's complete data (users, posts, DMs, etc) using their own API. Maybe that's how they got the info?
Most of those who were emailed had never installed this add-on; the contact details were apparently obtained through some other mechanism.
 
Most of those who were emailed had never installed this add-on; the contact details were apparently obtained through some other mechanism.
Yeah, I was one of the ones who got an email and I never installed it. No clue how they got my info cause I'd never even heard of this add-on until then. I was thinking maybe we're all members of other sites that did install this add-on. Again, I'm not even sure if that's possible but it appears as it is to me.
 
Propably to members that have their forum url on profile or in signature and then just tried commonly used emails. We also recieved one.
 
I'm surprised that, with so many affected users and the addon author's refusal to respond to them, not a single negative review has been posted about it yet...
 
Propably to members that have their forum url on profile or in signature and then just tried commonly used emails. We also recieved one.

Why?

If i send to admin@yourforum.com i could get a hit.
I don’t think you fully understood what I was explaining earlier. The issue is that we were contacted through an internal business email address that was never public and was only ever associated with a specific XenForo license. This wasn’t some generic contact address that could simply be found online or even guessed.

As I mentioned previously, it’s entirely possible that another third-party vendor we had worked with in the past may have had access to some of this information. However, @forumcopilot could not have randomly identified us while also knowing the exact license name and the exact business email address tied specifically to that license. That level of detail had to come from somewhere.

For additional clarity, we did not download, install, view, or even know this addon existed until the rather auspicious sales email arrived at a private address.
 
Last edited:
I decided to dig through the code a bit since I did install this earlier and uninstalled it. It does send some information during install to this endpoint: https://forumcopilot.com/api/register-site-public. It captures the board's name, URL, description, and attempts to capture the email of whoever installed the add-on.

I don't necessarily think anything malicious was intended since the author has clearly left comments detailing what the code is doing, but regardless this needs to be disclosed.

The one concerning part of this, is that it this is also duplicated in Options/SiteInfoForm.php which means whichever admin accesses the options and hits save, their email also gets send to ForumCopilots server. Again, I don't want to assume anything malicious was intended, this could of just been an after thought.
Code:
private function registerWithForumCopilot()
    {
        try
        {
            $app = \XF::app();
            $options = $app->options();
        
            $apiUrl = BackendApi::API_URL . '/register-site-public';
        
            $boardUrl = rtrim($options->boardUrl, '/');
            $boardTitle = $options->boardTitle ?? 'Community Forum';
            $boardDescription = $options->boardDescription ?? 'Community Forum';
        
            // Get email of the user installing the plugin (current visitor/admin)
            $techContact = null;
            try
            {
                $visitor = \XF::visitor();
                if ($visitor && $visitor->user_id > 0 && !empty($visitor->email))
                {
                    $techContact = $visitor->email;
                }
            }
            catch (\Throwable $e)
            {
                // If we can't get visitor email, continue without it
            }
        
            $data = [
                'name' => $boardTitle,
                'url' => $boardUrl,
                'description' => $boardDescription,
                'endpoint' => 'forumcopilot.php',
                'provider' => 'xenforo'
            ];
        
            // Add tech_contact if available
            if ($techContact)
            {
                $data['tech_contact'] = $techContact;
            }
        
            $ch = curl_init($apiUrl);
            curl_setopt_array($ch, [
                CURLOPT_RETURNTRANSFER => true,
                CURLOPT_POST => true,
                CURLOPT_POSTFIELDS => json_encode($data),
                CURLOPT_HTTPHEADER => [
                    'Content-Type: application/json',
                    'User-Agent: ' . BackendApi::USER_AGENT
                ],
                CURLOPT_TIMEOUT => 10,
                CURLOPT_SSL_VERIFYPEER => true
            ]);
        
            $response = curl_exec($ch);
            $httpCode = curl_getinfo($ch, CURLINFO_HTTP_CODE);
            $curlError = curl_error($ch);
            curl_close($ch);
        
            if ($curlError)
            {
                \XF::logError('ForumCopilot registration failed: Connection error - ' . $curlError);
                return;
            }
        
            if ($httpCode === 200)
            {
                $result = json_decode($response, true);
                if ($result && isset($result['site_id']))
                {
                    $siteId = $result['site_id'];
                    $apikey = $result['apikey'] ?? null;
                    $created = $result['created'] ?? false;
                
                    // Store site_id and apikey in options (use fc_push_api_key)
                    try {
                        $optionRepo = $app->repository('XF:Option');
                    
                        // Use updateOptions which is the proper way to update options
                        $updateData = ['fc_site_id' => (string)$siteId];
                        if ($apikey) {
                            $updateData['fc_push_api_key'] = $apikey;
                        }
                    
                        $optionRepo->updateOptions($updateData);
                    } catch (\Throwable $e) {
                        \XF::logError('ForumCopilot registration: Failed to save options - ' . $e->getMessage() . ' - site_id=' . $siteId . ($apikey ? ', apikey=' . $apikey : '') . ' - Trace: ' . $e->getTraceAsString());
                    }
                }
                else
                {
                    \XF::logError('ForumCopilot registration failed: Invalid response format - ' . $response);
                }
            }
            else
            {
                $errorData = json_decode($response, true);
                $errorMessage = $errorData['error'] ?? 'Unknown error';
                \XF::logError('ForumCopilot registration failed: HTTP ' . $httpCode . ' - ' . $errorMessage);
            }
        }
        catch (\Throwable $e)
        {
            // Log error but don't break installation
            \XF::logError('ForumCopilot registration failed: ' . $e->getMessage());
        }
    }
 
The email I got was not addressed to the email I use here.
It was a different email-address which I have never used here.
 
Last edited:
Hey,

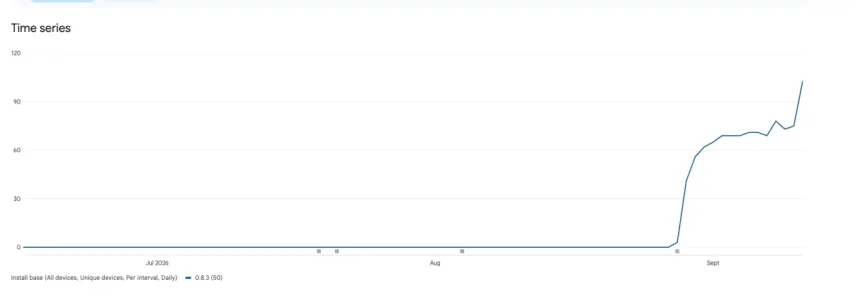
I've been using Forumcopilot's app on Android + iOS for roughly a month Screenshot 2026-09-14 at 12-09-35 Statistics QHHT Forum.webp

The client in question doesn't have a huge forum, it's actually a paid forum.

We've not just used the app, but hired Peter / Forumcopilot to do some custom work on the app to suit the client's experience more, and honestly I can't thank him enough for the work he's done, we've had calls, we've worked together on Whatsapp, he's been fantastic.

I suspect the code has no malicious intent, I have pointed him to this thread just so he can explain the route himself
 
Hey, sorry - we’ve been underwater for the past few weeks, not only delivering the project for @DigitalME but also working on a few other things.

We’re wrapping up another major update to this open-source forum app. It should also address @matt c.’s concern about our ability to retrieve the forum owner’s email address. This feature was designed solely to send you a verification link after you install the add-on, allowing us to begin delivering push notifications to your members. There is absolutely nothing malicious about it.

A quick reminder this is the link to the App source code:

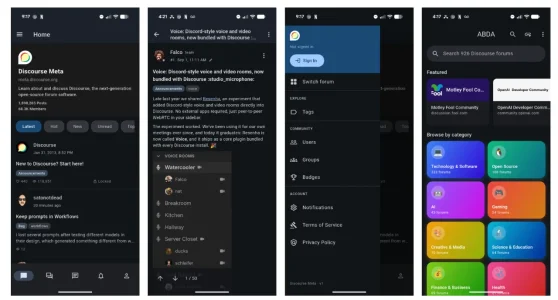
Also a shameless plug we also finishing up the similar app, natively for Discourse forum platform (Hopefully the admin here is okay that I mention it:


Screenshot 2026-09-17 at 4.38.58 PM.webp
 
forumcopilot updated Forum Copilot Open Source Mobile App with a new update entry:

1.8.5: XenForo 2.2 and 2.3 verified, reactions, PM push, and the app is now free

The Forum Copilot app is now free. The former $4.99 purchase and the hosted push service are both free for every forum. Nothing to configure on your side.

What changed in the add-on (1.4.0 to 1.8.5)
  • Reactions. The app shows your forum's full reaction set with a tap-to-choose picker and a "who reacted" list. Built-in reactions map to native emoji on both 2.2 and 2.3; custom reactions use their emoji replacement or image.
  • Private-conversation push notifications now...

Read the rest of this update entry...
 
@forumcopilot Getting a lot of server errors with that update:
Code:
ErrorException: [FC DEBUG] AlertPushProcessor: SKIP — no recipients have app installed (xf_fc_user.last_seen within 90d). Recipient IDs: 123456
src/XF/Error.php:81
Generated by: Unknown account
Sep 25, 2026 at 1:47 PM

Stack trace:
#0 src/XF.php(270): XF\Error->logError('[FC DEBUG] Aler...', false)
#1 src/addons/ForumCopilot/Service/Alert/AlertPushProcessor.php(62): XF::logError('[FC DEBUG] Aler...')
#2 src/addons/ForumCopilot/Job/ProcessAlertPush.php(26): ForumCopilot\Service\Alert\AlertPushProcessor->processCollectedAlerts(Array)
#3 src/XF/Job/Manager.php(275): ForumCopilot\Job\ProcessAlertPush->run(8)
#4 src/XF/Job/Manager.php(205): XF\Job\Manager->runJobInternal(Array, 8)
#5 src/XF/Job/Manager.php(89): XF\Job\Manager->runJobEntry(Array, 8)
#6 job.php(46): XF\Job\Manager->runQueue(false, 8)
#7 {main}

Request state
array(4) {
  ["url"] => string(8) "/job.php"
  ["referrer"] => string(80) "https://www.domain.com/threads/testthread.471173/page-8572"
  ["_GET"] => array(0) {
  }
  ["_POST"] => array(0) {
  }
}

And
Code:
ErrorException: [FC DEBUG] AlertPushProcessor: 1 collected alert(s) for 1 unique receiver(s) [276279]
src/XF/Error.php:81
Generated by: Unknown account
Sep 25, 2026 at 1:47 PM

Stack trace
#0 src/XF.php(270): XF\Error->logError('[FC DEBUG] Aler...', false)
#1 src/addons/ForumCopilot/Service/Alert/AlertPushProcessor.php(42): XF::logError('[FC DEBUG] Aler...')
#2 src/addons/ForumCopilot/Job/ProcessAlertPush.php(26): ForumCopilot\Service\Alert\AlertPushProcessor->processCollectedAlerts(Array)
#3 src/XF/Job/Manager.php(275): ForumCopilot\Job\ProcessAlertPush->run(8)
#4 src/XF/Job/Manager.php(205): XF\Job\Manager->runJobInternal(Array, 8)
#5 src/XF/Job/Manager.php(89): XF\Job\Manager->runJobEntry(Array, 8)
#6 job.php(46): XF\Job\Manager->runQueue(false, 8)
#7 {main}

And

Code:
ErrorException: [FC DEBUG] AlertPushProcessor: 0/1 receiver(s) have app installed []
src/XF/Error.php:81
Generated by: Unknown account
Sep 25, 2026 at 1:47 PM

Stack trace
#0 src/XF.php(270): XF\Error->logError('[FC DEBUG] Aler...', false)
#1 src/addons/ForumCopilot/Service/Alert/AlertPushProcessor.php(55): XF::logError('[FC DEBUG] Aler...')
#2 src/addons/ForumCopilot/Job/ProcessAlertPush.php(26): ForumCopilot\Service\Alert\AlertPushProcessor->processCollectedAlerts(Array)
#3 src/XF/Job/Manager.php(275): ForumCopilot\Job\ProcessAlertPush->run(8)
#4 src/XF/Job/Manager.php(205): XF\Job\Manager->runJobInternal(Array, 8)
#5 src/XF/Job/Manager.php(89): XF\Job\Manager->runJobEntry(Array, 8)
#6 job.php(46): XF\Job\Manager->runQueue(false, 8)
#7 {main}
 
It should also address @matt c.’s concern about our ability to retrieve the forum owner’s email address. This feature was designed solely to send you a verification link after you install the add-on, allowing us to begin delivering push notifications to your members. There is absolutely nothing malicious about it.

This does not explain the spam mails that you sent out earlier to people who have not even installed the add on. Did I miss an explanation for that?

we were contacted unexpectedly using license-related information that was never provided to this developer directly. We never opted into, subscribed to, or requested any form of marketing communication from them in the first place.

Most of those who were emailed had never installed this add-on; the contact details were apparently obtained through some other mechanism.

I was one of the ones who got an email and I never installed it.
 
Back
Top Bottom