Fortunately, Roku, which has the largest (28% of TVs), doesn't allow proxies. That said, there are a scary number of exploited TVs out there!

Fortunately, Roku, which has the largest (28% of TVs), doesn't allow proxies. That said, there are a scary number of exploited TVs out there!

Fortunately, Roku, which has the largest (28% of TVs), doesn't allow proxies. That said, there are a scary number of exploited TVs out there!
Really? we use a Roku... maybe i don't have to convert my TV to be desktop computer driven..

bash -lc python - <<'PY'
import requests
urls=['https://www.totaltools.com.au/catalogsearch/result/?q=battery+isolator','https://www.totaltools.com.au/search?q=battery+isolator','https://www.totaltools.com.au/catalogsearch/result/?q=isolator']
for u in urls:
    r=requests.get(u,headers={'User-Agent':'Mozilla/5.0'},timeout=20)
    print(u,r.status_code,r.url,len(r.text),r.text[:200])
PYSo far for the honesty of the big AI providers and their models and the claim that they would act transparently with their AIs. It is really sickening how the AI companies force the internet to change to a world of distrust and locked doors and deny any responsibility just to foster their own profit.A very crude user-agent spoof.
BTW: Possibly the world starts to slowly wake up regarding scrapers. Over the last weeks I recognized anti-bot measures on websites and forums all over the place on sites that had been freely accessible / unprotected until now. Seems to be a change at scale and started only recently.

Ah.. I know what you're talking about. Does it create random fields for guest posting? I stopped using those sort of things long ago, as it was one of the first things bot got around. Saying that... sometimes old school works well because they all moved on from it. How many times have flares come back!It creates random fields for registration, login and contact forms that only a bot would see and fill in.

in opposite to what one could assume it works pretty excellently. It blocked thousands of spam registrations in my forum and in others as well as you can see in the thread for the add on:I stopped using those sort of things long ago, as it was one of the first things bot got around.
This addon is another tool in fighting spam bot registrations at your forum.
How it works
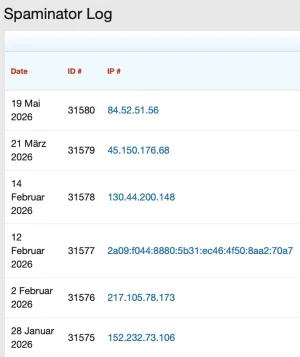
The [OzzModz] Registration Spaminator injects false fields and checkboxes into the registration form which browsers don't render so humans never see. But the bots fill out the fields and check the boxes - identifying themselves as bots and falling into the Spaminator trap. The Spaminator then logs all the information and sends the bots to register-complete...


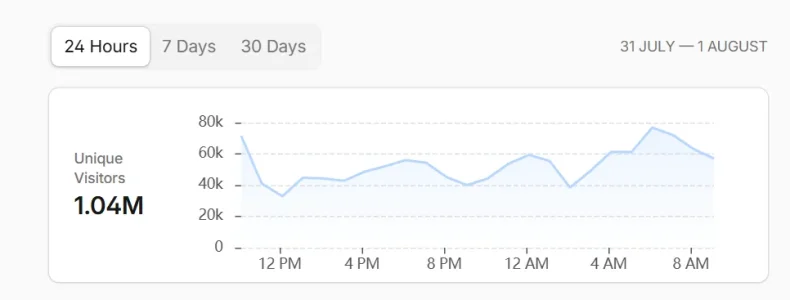
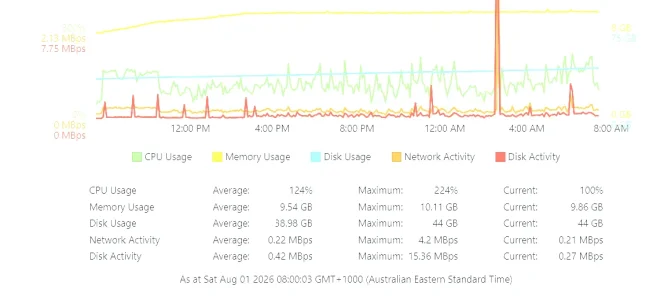
 (centminmod optimised) I wanted to see how it handled, so I disabled the residential proxy rule... 2.25 cpu cores at peak. Easy. It handled 300vu/ps with ease during setup testing (3 million daily equivalent), but its nice to see real world load, where all variables are in play.
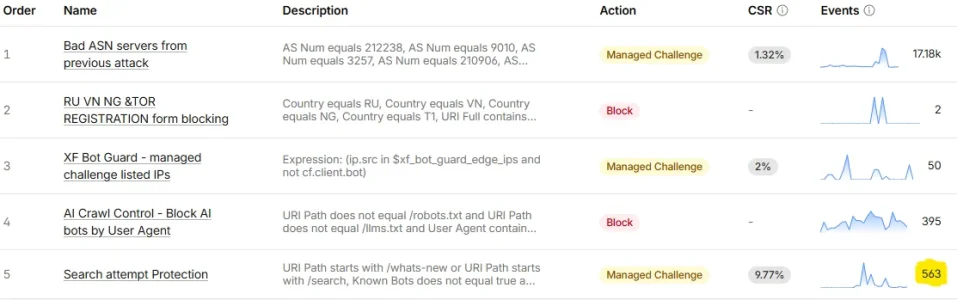
(starts_with(http.request.uri.path, "/whats-new") or starts_with(http.request.uri.path, "/search"))
and not cf.client.bot
and not http.cookie contains "xf_user="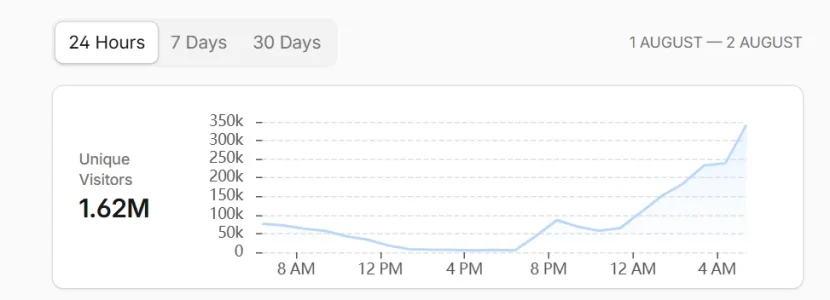
(http.user_agent contains "Chrome/99." or http.user_agent contains "Chrome/100." or http.user_agent contains "Chrome/101." or http.user_agent contains "Chrome/103." or http.user_agent contains "Chrome/104." or http.user_agent contains "Chrome/105." or http.user_agent contains "Chrome/106." or http.user_agent contains "Chrome/107." or http.user_agent contains "Chrome/108." or http.user_agent contains "Chrome/109." or http.user_agent contains "Chrome/110." or http.user_agent contains "Chrome/112." or http.user_agent contains "Chrome/116." or http.user_agent contains "Chrome/119." or http.user_agent contains "Chrome/120." or http.user_agent contains "Chrome/123." or http.user_agent contains "Chrome/124." or http.user_agent contains "Chrome/131." or http.user_agent contains "Chrome/133." or http.user_agent contains "Chrome/136." or http.user_agent contains "Chrome/142." or http.user_agent contains "Chrome/143." or http.user_agent contains "Chrome/144." or http.user_agent contains "Chrome/145." or http.user_agent contains "Chrome/146." or http.user_agent contains "Chrome/65." or http.user_agent contains "Firefox/133." or http.user_agent contains "Firefox/135." or http.user_agent contains "Firefox/144." or http.user_agent contains "Firefox/147.") and http.referer eq "" and (not cf.client.bot) and (not http.cookie contains "xf_user")
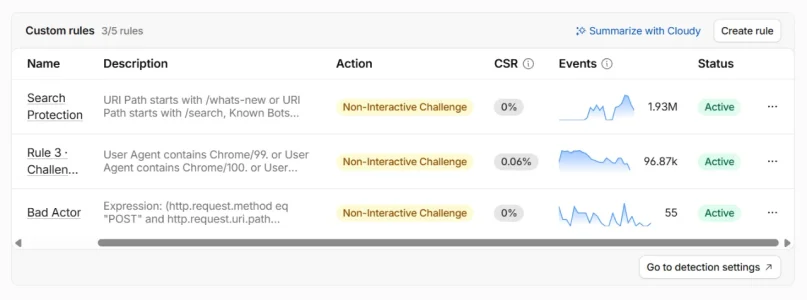
That rule is gold. I finally got attacked, and that rule saved my bacon. 5000 a minute attempt... CF for the win on a non-interactive challenge. I have been waiting soooooo long for this data. Its still going as I speak... but the data is amazing.Code:(starts_with(http.request.uri.path, "/whats-new") or starts_with(http.request.uri.path, "/search")) and not cf.client.bot and not http.cookie contains "xf_user="
View attachment 342138
I'm starting to think they're watching this thread! They shifted to Chrome/143 and Chrome/144 which I didn't have covered, but do now, yet the load bearing /search rule is there for this exact reason.
Code:(http.user_agent contains "Chrome/99." or http.user_agent contains "Chrome/100." or http.user_agent contains "Chrome/101." or http.user_agent contains "Chrome/103." or http.user_agent contains "Chrome/104." or http.user_agent contains "Chrome/105." or http.user_agent contains "Chrome/106." or http.user_agent contains "Chrome/107." or http.user_agent contains "Chrome/108." or http.user_agent contains "Chrome/109." or http.user_agent contains "Chrome/110." or http.user_agent contains "Chrome/112." or http.user_agent contains "Chrome/116." or http.user_agent contains "Chrome/119." or http.user_agent contains "Chrome/120." or http.user_agent contains "Chrome/123." or http.user_agent contains "Chrome/124." or http.user_agent contains "Chrome/131." or http.user_agent contains "Chrome/133." or http.user_agent contains "Chrome/136." or http.user_agent contains "Chrome/142." or http.user_agent contains "Chrome/143." or http.user_agent contains "Chrome/144." or http.user_agent contains "Chrome/145." or http.user_agent contains "Chrome/146." or http.user_agent contains "Chrome/65." or http.user_agent contains "Firefox/133." or http.user_agent contains "Firefox/135." or http.user_agent contains "Firefox/144." or http.user_agent contains "Firefox/147.") and http.referer eq "" and (not cf.client.bot) and (not http.cookie contains "xf_user")
I have all my rules set to non-interactive challenge, so no real person is ever disrupted using the site. I was so excited to see an attack, finally... as I've been wanting good data.Are you using that rule with a BLOCK or an INTERACTIVE CHALLENGE? I have it set up with the second, but no bites so far.
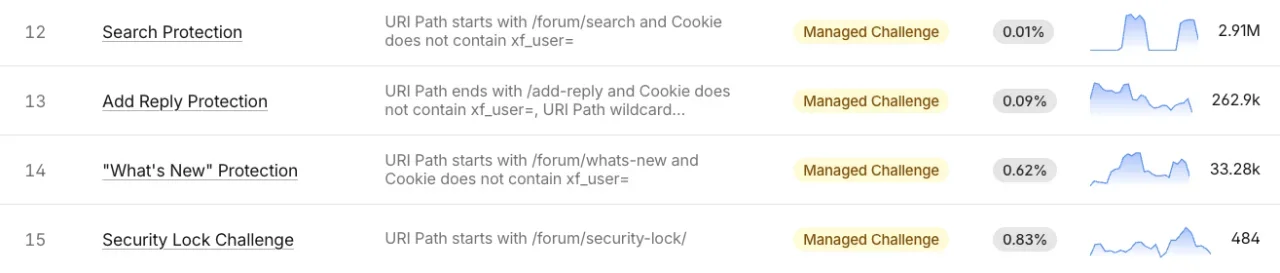
That is some serious abusive attempt to take out your server.2.91M requests to /forum/search with a 0.01% solve rate...

It seems they're on a rampage... and /search is just malicious, crawlers aren't hammering search, they just move from page to page, they don't need search. I'm happy though... as I'm getting good data to continuously improve my heuristics scoring. I've never had this much on search though... which really just seem malicious to me... well, attempted and thwarted automatically, yet malicious.2.91M requests to /forum/search with a 0.01% solve rate...


We use essential cookies to make this site work, and optional cookies to enhance your experience.