Anthony,
I have watched this page with interest but overwhelmed with the amount of info. I have cloudflare account and have a few simple securities rules set up there.
What types of rules are you setting here?
Managed rules, custom rules, IP access rules?
Managed rules are cloudflare, primarily, upgraded accounts allows you to make changes and add CF managed rules to your site. Custom rules are what most people use when creating a rule for their website.
Thank you for the link about Turnstile - I don't fully understand the article - it sounds complicated.
Turnstile is more applicable to stopping human spam on your site. If you had a human spam problem, turnstile can solve that automagically for you by placing turnstile into every POST, for example. Instead of a page failing, XF reloads via ajax, on posting a cookie is presented to the browser. If its not a real person sitting there, fail. If it is, success. This stops spammers registering, posting a few times, getting past human moderation, then handing an account to software to go nuts and spam the site. Member, guest, turnstile just works behind the scenes.
Turnstile helps on things like registration, posts, searches, etc. It does not help on stopping bots scraping your site, that is a different problem.
I'm still a bit confused about the skip list. It includes Baiduspider - would I really want that? I've had it blocked in .htaccess for a long time. Also - I don't understand what "lower" in there means.
I posted earlier my actual list.
https://xenforo.com/community/threads/crazy-amount-of-guests.233649/page-87#post-1796967
You questioned it here:
https://xenforo.com/community/threads/crazy-amount-of-guests.233649/page-87#post-1797018
I responded with an extended list if you wanted global coverage... though yes, if you don't want China, Korea, Russia, etc, then go back to my original list of essentials.
A quirky thought, if these people building scrapers, can get a list of residential proxies, like on that video, couldn't we get the same list of residential proxies and block them?
No. Residential IP's change. I have already proven you can adequately block residential proxies by targeting header information. Saying that, if someone goes balls to the wall and completely spoofs a real browser, fingerprint, cookies, javascript, behaviour, combined with residential proxies, then its a sitewide managed challenge for every visitor pretty much. That would be the only way to stop it at that level. Right now... most aren't mimicking the full browser specifics needed, nor the behaviour. You can catch both easily and target it. If they fix that and stop being greedy, then it shifts to Very Difficult.
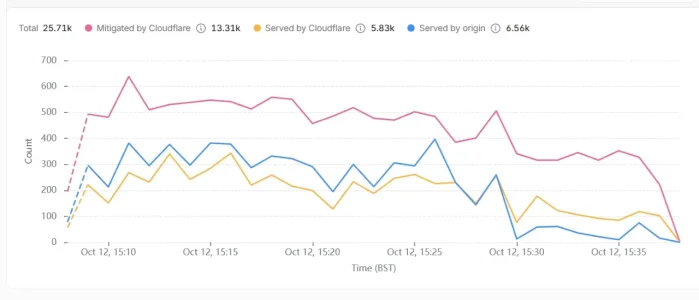
How can we consolidate the numbers reported by XF online users vs Google analytics real time users.
View attachment 347045View attachment 347046
Your realtime users, are probably more like 1-10 online at any given time.
Had another idea. Out of the 1.37 million requests, 1.31 million of them are from desktop - and as they all hit Whats new then maybe I could just block anything using desktop and trying to access whats new, while whitelisting registered members and known bots. While this does run the risk of blocking a genuine guest from whats new, it's probably a low risk as most genuine users use mobiles.
So a block rule:
(cf.client.device_type eq "desktop" and http.request.uri.path contains "/whats-new/" and not http.cookie contains "xf_user" and not cf.client.bot)
Any thoughts?
Yer, don't try and target requests. Desktop is not identification of a person or bot, xf_user does not authenticate a member either and you would block guest humans from whats new. Also, CF requests does not mean the request reached your server, it would record it from CF cache I believe.
A request is not a user either, one page load can be 30 to 80 requests.
If you had 40 requests per page load, your requests, that is roughly 34k pages.