
You are using an out of date browser. It may not display this or other websites correctly.
You should upgrade or use an alternative browser.
You should upgrade or use an alternative browser.
Crazy amount of guests
- Thread starter Levina
- Start date
-
- Tags
- bot swarms guests

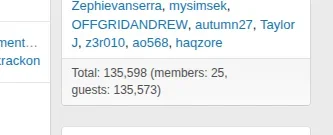
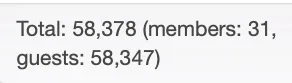
Here at XF right now:
The forum seems somewhat slowish to a degree atm sometimes and a couple of minutes ago I got this:
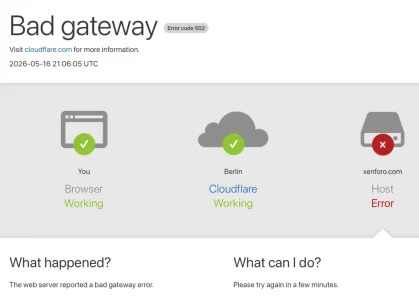
So possibly the bots start to hit the resource limits of the XF forum.
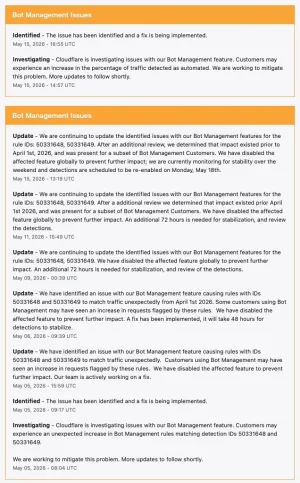
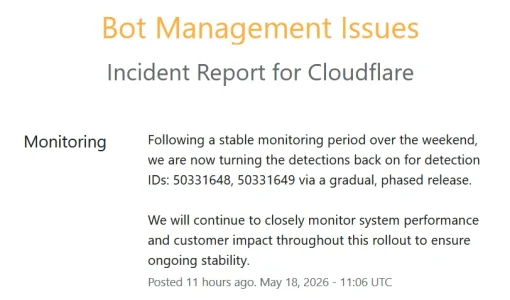
CF bot management is still somewhat defective, according to their status page:

The forum seems somewhat slowish to a degree atm sometimes and a couple of minutes ago I got this:
So possibly the bots start to hit the resource limits of the XF forum.
CF bot management is still somewhat defective, according to their status page:
Last edited:

Yes, it’s been taking ~10 seconds to get a page to render from this thread.Here at XF right now:
View attachment 337800
The forum seems somewhat slowish to a degree atm sometimes and a couple of minutes ago I got this:
View attachment 337802
So possibly the bots start to hit the resource limits of the XF forum.
Has anyone here implemented this block list?

 github.com
GitHub - borestad/blocklist-abuseipdb: Aggregated AbuseIPDB blocklists with worst IPv4 & IPv6 offenders (~99% confidence)
Aggregated AbuseIPDB blocklists with worst IPv4 & IPv6 offenders (~99% confidence) - borestad/blocklist-abuseipdb
github.com

I just want to say, that this is testament to this thread. They try really hard on my site, but ultimately fail each time. They gave it a good shot twice in the last 24hrs, very short lived on both, all due to this thread contents.
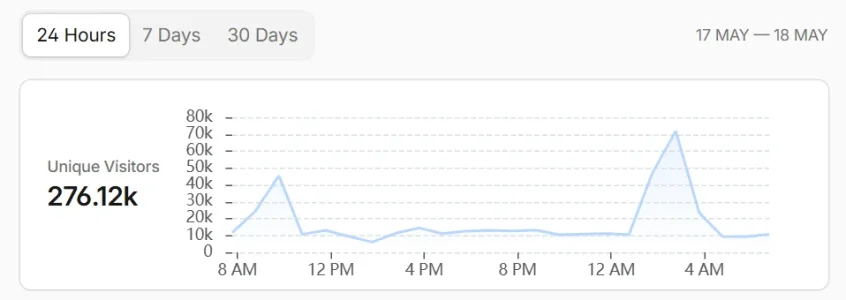

We had around 36,000 'guests' on the site last night.
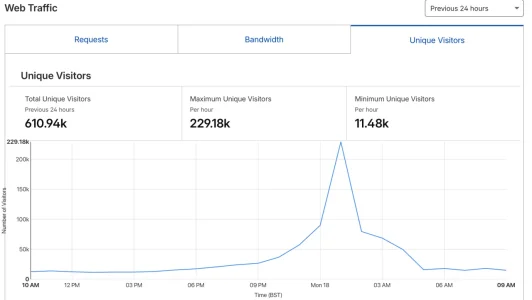
After engaging Cloudflare's 'under attack' mode, at its peak, around 00:42 we had 245.9K unique visitors hitting the Cloudflare firewall with 364+K simultaneous server hits.
I've got various filters and rules in place, which up to now have been reasonably efficient, but last night was an exception
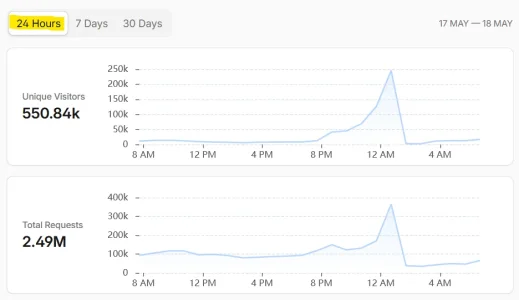
After engaging Cloudflare's 'under attack' mode, at its peak, around 00:42 we had 245.9K unique visitors hitting the Cloudflare firewall with 364+K simultaneous server hits.
I've got various filters and rules in place, which up to now have been reasonably efficient, but last night was an exception
I didn't do that, they gave up on their own getting error page after error page, but if it works, use it.After engaging Cloudflare's 'under attack' mode
Very similar pattern on our site too, including the timing, though we didn't turn on UAM.We had around 36,000 'guests' on the site last night.
After engaging Cloudflare's 'under attack' mode, at its peak, around 00:42 we had 245.9K unique visitors hitting the Cloudflare firewall with 364+K simultaneous server hits.
I've got various filters and rules in place, which up to now have been reasonably efficient, but last night was an exception
View attachment 338001
We used it for some time but now only firehol blocklist.Has anyone here implemented this block list?
GitHub - borestad/blocklist-abuseipdb: Aggregated AbuseIPDB blocklists with worst IPv4 & IPv6 offenders (~99% confidence)
Aggregated AbuseIPDB blocklists with worst IPv4 & IPv6 offenders (~99% confidence) - borestad/blocklist-abuseipdb
6-24% of those ip's are in firehol depending of the level.
Last edited:
If it helps anyone, I use this add-on for quick access to Cloudflare:
It basically covers most of what's needed without the bulk you find on Cloudflare dashboard
However setting rules is best done on CF in my opinion
One benefit of the add-on is that you can block individual countries, quickly and without complication. So when looking down the XF 'Guests' list and then using 'Manage country blocking' you can select countries that you are seeing guests from that you know have nothing to offer your site


Configure and manage your Cloudflare account from within XenForo.
It basically covers most of what's needed without the bulk you find on Cloudflare dashboard
However setting rules is best done on CF in my opinion
One benefit of the add-on is that you can block individual countries, quickly and without complication. So when looking down the XF 'Guests' list and then using 'Manage country blocking' you can select countries that you are seeing guests from that you know have nothing to offer your site
I found a new kid on the block today in my logs: A bunch of IPs coming from "AS59651 Alex Largman", registered in Israel and partly subleased to a "Beyond Tomorrow Ltd", trying to gain access from various countries. Had not had this ASN in my logs before, so I became a bit curious. As often, a lot remains unclear but then I found a bit of gold. Upon other findings the name showed up in an article that followed the path of a DDOS attack in 2023 and discussed the involvement of companies selling proxy access in those attacks and followed the path to trace down the people behind these companies.
Alex Largman turned out to have changed his name from "Aleksey Bulgakov" and is the founder of a company named "Fast Internet LLC" - he even has a Github account under this name. There is a company with this name run by a person named Alex Largman registered in the UK and classified as a micro company. According to the article...
... most of the players behind these services seem to come from Russia (and some from the US) and have a long history when it comes to dubious and fraudulent activities on the internet. It is a pretty interesting read how they found short-lived companies around the world to gain IP-netblocks and cover their activities, how involved they are in attacks with their proxy companies and how "ethical" their sourcing really is.
Quirium regularly posts forensics about DDOS attacks and I cross read a couple of those, only to find more proxy companies to be involved - any many of the company names mentioned sounded pretty familiar. Like these here:
I.e. in one article 3xK Tech GmbH showed, a company from Germany that I mentioned way further up this thread as it seemed a bit of a strange company - until today they are a regular guest in my log files for blocked access attempts:
So the assumptions that these proxy companies are pretty shady for the most part seem to be justified - they seem to be even more involved in scam, fraud, DDOS etc. than we discussed in the past.
Alex Largman turned out to have changed his name from "Aleksey Bulgakov" and is the founder of a company named "Fast Internet LLC" - he even has a Github account under this name. There is a company with this name run by a person named Alex Largman registered in the UK and classified as a micro company. According to the article...

... most of the players behind these services seem to come from Russia (and some from the US) and have a long history when it comes to dubious and fraudulent activities on the internet. It is a pretty interesting read how they found short-lived companies around the world to gain IP-netblocks and cover their activities, how involved they are in attacks with their proxy companies and how "ethical" their sourcing really is.
Quirium regularly posts forensics about DDOS attacks and I cross read a couple of those, only to find more proxy companies to be involved - any many of the company names mentioned sounded pretty familiar. Like these here:
I.e. in one article 3xK Tech GmbH showed, a company from Germany that I mentioned way further up this thread as it seemed a bit of a strange company - until today they are a regular guest in my log files for blocked access attempts:
So the assumptions that these proxy companies are pretty shady for the most part seem to be justified - they seem to be even more involved in scam, fraud, DDOS etc. than we discussed in the past.
Last edited:

What continues to puzzle me is why i'm not seeing any of this using fail2ban.
Using that as a sole protection mechanism has numerous weak points, but we still consistently see good numbers, and no gigaspikes.
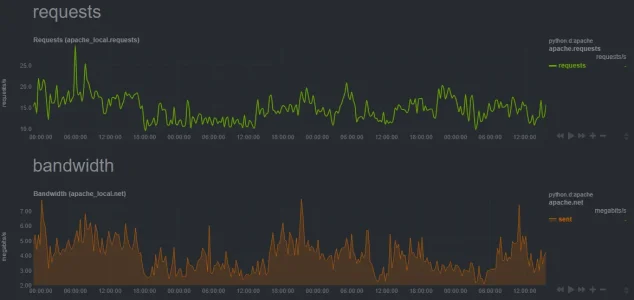
Netdata says this about my traffic over the last couple days:
I would guess that someone's figured out ways around cloudflare. And their IP pool is enormous.
At least some configuration exists to make CF work well enough.
Using that as a sole protection mechanism has numerous weak points, but we still consistently see good numbers, and no gigaspikes.
Netdata says this about my traffic over the last couple days:
I would guess that someone's figured out ways around cloudflare. And their IP pool is enormous.
At least some configuration exists to make CF work well enough.
My forum is now experiencing a large number of guests (33k and climbing), despite banning lots of countries and blocking several robots.
Pretty much echoing last night's increase in traffic, about the same time.
I've changed the Cloudflare security level from High to UAM as the increase is starting to affect page loading times.
Update: Now down to 147 guests from 33k+ , 30minutes from implementing UAM
Pretty much echoing last night's increase in traffic, about the same time.
I've changed the Cloudflare security level from High to UAM as the increase is starting to affect page loading times.
Update: Now down to 147 guests from 33k+ , 30minutes from implementing UAM
Last edited:

If they're hammering your server(s), probably best to just implement something like Anubis and adding a whitelist check for existing XF2 cookies for a bypass.My forum is now experiencing a large number of guests (33k and climbing), despite banning lots of countries and blocking several robots.
Pretty much echoing last night's increase in traffic, about the same time.
I've changed the Cloudflare security level from High to UAM as the increase is starting to affect page loading times.
If you are running apache or nginx, you can use this to analyze your traffic by pointing this to your access log.
I have used these scripts for a few years and used deepseek to write them per my design.
These will reveal the IPs/hostnames of your most frequent 'visitors'. I use it to collect information on what ASNs i need to ban manually in .htaccess.
What i bet you are going to find is tons of residential proxies in the country your firewall allows.
Warning: this script can take some time to compute a super busy log. Make sure to run it during a slow time!
Attachments
Last edited:
It is btw. worth blocking this ASN altogether. I've seen it yesterday for the first time in the proxycheck.io logs for identified proxies but was not bothered enough for the moment to block the complete ASN. When I just looked at my live access log I saw literally dozens of different IPs from that ASN visiting my forum in parallel while within the same timeframe proxycheck had identified only 2 IPs from this ASN to be proxies or other malicious machines.I found a new kid on the block today in my logs: A bunch of IPs coming from "AS59651 Alex Largman", registered in Israel and partly subleased to a "Beyond Tomorrow Ltd", trying to gain access from various countries. Had not had this ASN in my logs before
As there is no way that "good" or desired traffic is coming from this ASN this means: Proxycheck currently only detects a fraction of the bots coming from there and lets 90-99% through. Therefore banning the whole ASN manually is the best strategy and adequate as well w/o any collateral damage.

Similar threads
- Replies
- 6
- Views
- 189


- Replies
- 8
- Views
- 222

