Serious concern: Why were XenForo customers never informed about this alleged internal data leak?

Status
Not open for further replies.

Starbucks

Well-known member
Licensed customer
Hi,

I just saw this post on TheAdminZone: https://www.theadminzone.com/threads/i-assume-this-is-not-good-news-for-xenforo.156931/ about the Northern Ireland High Court case involving Tattle Life, and honestly this I find this pretty concerning as a XenForo customer.

According to the judgment (Sands & Anor v Bond & Ors [2026] NIHC KB 20), there was apparently a “confidential source who appears to have been working for XenForo” leaking customer information before any court order was even issued.

The leaked information allegedly included:
  • Purchase orders from multiple years
  • Real names
  • Email addresses
  • Postcodes
  • Internal hosting/server related information
What concerns me the most is not even the lawsuit itself, but the fact that I can’t find any public communication from XenForo about this situation.

If customer billing data and purchase history was accessible to someone internally and shared externally without a legal order, then why were customers not informed?

Was there an internal investigation?
Were affected customers contacted?
What changes were made internally after this happened?

A lot of forum owners specifically rely on privacy and operational separation. Some communities discuss sensitive or controversial topics, and this case basically shows that even if someone protects their infrastructure externally, their identity may still be exposed through vendor-side records.

I’m not trying to start drama here. I genuinely want transparency.

Can XenForo clarify:
  • Whether customer data was improperly accessed?
  • Whether this was reported internally as a data breach?
  • Whether customers were notified?
  • What protections now exist against insider access/leaks?

Because from the outside, this feels like something customers should have been informed about directly.
 
I think your thread headline is misleading.

A lot of forum owners specifically rely on privacy and operational separation. Some communities discuss sensitive or controversial topics, and this case basically shows that even if someone protects their infrastructure externally, their identity may still be exposed through vendor-side records.
Welcome to the real world. If you don't want to take responsibility for your actions in court better don't use your credit card and mail address to buy stuff for your - in this case obviously filthy - business that later gets sued successfully and obviously for a reason. Or simply avoid running a filthy business.

Maybe the context of what has happened is of interest and matters:

• a person ran a forum named "tattle life" for what reads as gossip about influencers and more or less prominent people
• according to the court: "Tattle Life describes itself as "a commentary website on public business social media accounts". It permits members of the public to comment and criticise individuals who "choose to monetise their personal life as a business", including so‑called influencers." One may imagine what that may mean in reality - possibly a plattform full of defamation and hate speech.
• this forum war run on XenForo (at least in earlier years) and run anonymously by someone who first hid behind a British Ltd. and then behind one in Hongkong.
• a female inlucencer and her husband felt they were badly insulted and defamated on this forum and tried to get hold of the owner to sue him
• they filed for 300.000GBP in 2023
• they won, so obviously, they had a case
• the defendant made huge sums from the forum, according to the court:
On the evidence before the court, the website receives millions of visits per month and generates an income through online advertising. At its peak, Tattle Life had an annual income of over £500,000.

Additional financial details:
Yuzu Zest Limited had a net asset balance of £601,000, all in cash, on 31 March 2023. Since its incorporation in 2019, the company had steadily accumulated cash reserves through advertising revenue for Tattle Life."
The company paid a large dividend of £140,000 to Mr Bond in December 2023, shortly after judgment had been entered in these proceedings against persons unknown.
Between April and August 2024, Yuzu Zest Limited made a number of transfers, totalling some US $90,000, to Kumquat Tree Limited, the third defendant. It had been incorporated in Hong Kong in February 2024.
On 2 September 2024 the company transferred £898,632 to Mr Bond and the following day two dividend payments, totalling £12,950, were also paid to him.
A resolution to wind the company up was passed on 27 September 2024 and Mr Bond swore a declaration of solvency which stated the expected surplus for distribution to be £903,000. At this time, the monies which had been transferred to Mr Bond were treated as being a director's loan.
On 10 July 2025 the liquidators prepared a statement of affairs which identified unsecured claims against the company (including the costs and damages in this action) of £1,392,053 with assets of just £7,567.95. On 30 July 2025 the members' voluntary liquidation was converted to a creditors' voluntary liquidation.

Mr Bond also gave an interview to Unherd magazine in September 2025 in which he admits using the name "Helen McDougal" as a pseudonym and stating that the website continues to generate income of some £20,000 per month, paid to a company in Hong Kong.

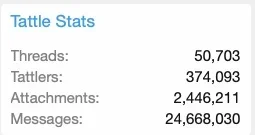
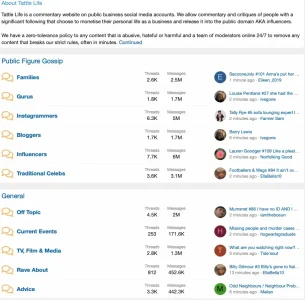
So we are clearly not talking about a small non-commercial hobby forum here or about SLAP or anything like that. Today, the website looks like this:

Bildschirmfoto 2026-05-20 um 22.34.54.webp

Bildschirmfoto 2026-05-20 um 22.35.34.webp


Xenforo has received a court order to lay open documents regarding the website like who bought the license for XenForo and other data that they may have regarding the case. They followed that order and this helped to give more evidence (there was evidence before) that the defendant ran the forum and was involved.

The issue is that an - according to the court - "source" from probably inside XenForo ( a confidential source who appears to have been working for Xenforo ) had given parts of this information to the plaintiffs or their lawyers before the court order had been made, earlier in the process. Nobody (publicly) knows who that was, nobody knows what the background for that may have been, all according to the document linked on Admin Zone.

Therefore it may be fair to ask what has happened and what the background was - but unfair to do this in the way you do it. And also, you'd have to live with an answer "this is none of your business", which would be totally ok in my eyes - but I'm sure you won't accept it.

I’m not trying to start drama here.
Yes, you do.
customers should have been informed about directly.
No. Why? It was a single case, three years ago, the data given would have been requested by the court later anyway. No other person affected. Data was not publicly released (but now has been by the court) but given to the plaintiffs (or their lawyer or investigator) in conjunction with a court case that seems to have been more than valid. This does not qualify as a "data leak" in the sense of GDPR. In case of a data breach those who are affected have legally to be informed. Well, he has been...
 
Last edited:
Forum Owner sued for defamation, XenForo testified in the case
So, as a secret staff member, be so kind to change the title for me. And no, don’t act like “why do you think I’m a secret staff member, you’re delusional blabla”, please just do it. It’s obvious who you are.

I don’t want you to write another novel for me, even tho I appreciate it <3
 
You're treading on thin ice here @Starbucks and not for the reason you will accuse me of.

If you're unable to participate in the forum in good faith and treat members with respect, we'll take the necessary action.

Presumably you are accusing @smallwheels of being "Jon" who is a member of staff on support who you just spoke to and a moderator here. That would be incorrect and really all that needs to be said on the matter.
 
Sometimes.
You're treading on thin ice here @Starbucks and not for the reason you will accuse me of.

If you're unable to participate in the forum in good faith and treat members with respect, we'll take the necessary action.

Presumably you are accusing @smallwheels of being "Jon" who is a member of staff on support who you just spoke to and a moderator here. That would be incorrect and really all that needs to be said on the matter.
So it took a little guess-game to get you out here to reply to my thread.

Can you then also formally reply to the question I asked or are we going forward with the “that’s none of your business”?

Also, you ruined the little game @smallwheels and I were playing because I did indeed expected him to be Jon.

I might be delusional after all.
 
I do think it’s concerning tho that you guys have a backdoor implemented in XenForo’s software that makes the staff to be able to get the data of every single customer @Chris D
 
So it took a little guess-game to get you out here to reply to my thread.

Can you then also formally reply to the question I asked or are we going forward with the “that’s none of your business”?

Also, you ruined the little game @smallwheels and I were playing because I did indeed expected him to be Jon.

I might be delusional after all.
If an official statement is to be made about anything then it will be made at an appropriate time by an appropriate person. To the best of my knowledge all of us in the company are hearing about this for the first time today.

People may of course wish to discuss it which is reasonable, but we will step in if the conversation is no longer respectful to its participants.
I hope you’ll then also look into the backdoor in the software that XenForo has, because that seems like a huge deal to me that every-single employee of XenForo LTD can just randomly login into each XenForo software admin panel.

At least that’s what I understood.
Correct me if I’m wrong.
 
I hope you’ll then also look into the backdoor in the software that XenForo has, because that seems like a huge deal to me that every-single employee of XenForo LTD can just randomly login into each XenForo software admin panel.
Do you have a source for such a claim? Because I've read the documents you've pointed people to and nothing mentions anything like that.

I would urge you to read and correctly comprehend what you're reading before making such baseless claims.
 
hope you’ll then also look into the backdoor in the software that XenForo has, because that seems like a huge deal to me that every-single employee of XenForo LTD can just randomly login into each XenForo software admin panel.
Think about this for a second: Every customer can download and install XF and look at the whole code base. There are a lot of experienced developers around here. I am quite sure, there would have been discussions already, if there was code inside the XF software package, that would allow an external server to take over a random XF installation.. In other words: any "backdoor" in XF would be part of the code, that any customer can download and I am sure it would not stay undiscovered for a long time. :rolleyes:
 
Status
Not open for further replies.
Back
Top Bottom