PSA: Critical PHP vulnerabilities

Why bother with "under maintenance" when Cloudflare already had a mitigation in place? My post earlier in this thread points to the blog post which says exactly that:

And as I also said, we all still need to update PHP but at least CF has our backs.

Cloudflare has been part of a coordinated effort to deploy mitigations to protect the Internet, working with PHP foundation, OpenAI and Wiz among others. Cloudflare has developed and deployed web application firewall (WAF) protections since early October 2026, which were deployed about 9 hours ahead of public disclosure. Starting on October 21 3:02 am UTC, Cloudflare customers using our free or paid WAF were protected by default against php2shell.
To deliver this protection, we developed full transaction detection, a new Cloudflare WAF capability that combines signals from the request and response within the same HTTP transaction. Response rules can then block a matching origin response before it reaches the requester. The php2shell protections are the first managed detections we have released using this capability.

Customers should patch their PHP repos even with WAF protections providing an additional layer of defense-in-depth mitigation. Our security analysts continue monitoring attack activity and update the rules when and if new techniques and variations emerge in the hours and days ahead. You can track new rules in the changelog.

The protections are available and deployed automatically on all plans with WAF deployed, including Free users.
 
"Matthew Prince, the boss of internet infrastructure firm Cloudflare, also said it had seen "thousands" of attempts to exploit the PHP vulnerabilities across its network in the 10 hours before it was publicly announced.

"That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within two hours, and millions now," he wrote on X, external."

 
Why bother with "under maintenance" when Cloudflare already had a mitigation in place? My post earlier in this thread points to the blog post which says exactly that:


And as I also said, we all still need to update PHP but at least CF has our backs.
CF is good for domain protection but what about if the content can be served directly via the IP? Cloudflare is useless then.
 
For those on WHM / cPanel just use the SSH terminal and issue

/usr/local/bin/ea4 --resync
What does that do? :-) Also is that just for ea.php and not alt.php?
I understand (I might be wrong) the delays with shared hosting, were waiting for the update from cpanel/cloudlinux
 
For those on WHM / cPanel just use the SSH terminal and issue

/usr/local/bin/ea4 --resync

I was at work when the PHP release dropped. cPanel had released their fixes, and my site was automatically updated, before I could even make it home to manually do it. Less than an hour, and maybe even less than a half-hour and my site was updated. Combined with the fact that only Cloudflare IPs can access my sites, and my domains were already protected by Cloudflare mitigation rules, and I should be good.

Still a little spooky though! Not really the Halloween scare I had in mind this year. 😂
If cpanel had fixes released then the delays must have been cloudlinux?
 
Update for Türkiye: The issue has been resolved in Türkiye. The necessary security updates and patches have been applied, and no further action is required from hosting customers.

Regarding the PHP vulnerabilities disclosed yesterday, we have taken the following actions:

  1. PHP versions on all shared servers have been updated and patched. No known vulnerabilities remain. Since CloudLinux provides security fixes for most PHP versions through backported patches, your own checks may make it appear that the versions have not been updated. However, the necessary patches have been applied, and the systems are not vulnerable.
  2. The control panels and PHP versions of all customers using our SLA3 server services have been updated. For customers who do not use SLA3, we logged in and performed the necessary updates wherever their registered access credentials were still valid. For customers using our Public Cloud (VPS) services, the updates were performed by accessing the nodes directly.
Despite our efforts to provide as much information as possible by email, it is extremely important for the security of customers whose servers we could not access to update their control panels and PHP versions themselves.

Customers using our hosting services do not need to take any action, and there is no reason for them to be concerned.

From the moment the issue was disclosed, we implemented the necessary PHP configuration changes and applied the updates as soon as the patches became available. As a result, we successfully addressed the incident without any security compromise.

For your information.
 
Essa pode ser a razão. Preciso registrar uma denúncia — a plataforma é XF?


@Chris D

@Paul B

Existe um site que está roubando anexos de fóruns que usam a plataforma XF.
Ele copia o link que contém o anexo e permite o download (não é necessário status VIP).


Anexos estão sendo roubados de três fóruns diferentes — todos eles utilizam a plataforma XF.
 
Last edited:
Forum replies should be in English.

What you are reporting is unrelated to the PHP security advisories.

If you’d like to discuss this issue in more detail it would be best to provide more information at https://xenforo.com/contact/
 
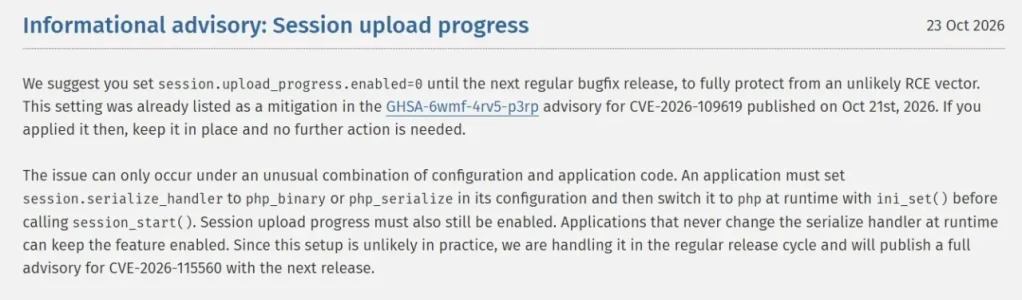
PHP dropping another security advisory, just two days after the last one. October is getting interesting for PHP 😅

1792768586191.webp
 
Back
Top Bottom