XF 2.3 PHP Emergency Patches & XenForo Cloud Status (CVE-2026-109618 / CVE-2026-109619)

jtb33

Member
Licensed customer

Hi XenForo Team and Community,

With the recent news regarding the upcoming critical emergency patches for PHP (CVE-2026-109618 and CVE-2026-109619) dropping imminently, I wanted to check in regarding the status for those of us who are XenForo Cloud customers.

Since the vulnerabilities are rated 9.2/10 and mass exploits are expected quickly following the 14:00 UTC release window, could the team clarify the patching window and deployment plan for the Cloud infrastructure?

Are these patches being rolled out automatically to all XenForo Cloud instances immediately upon release, and should we anticipate any brief downtime or maintenance windows when the underlying PHP environment is updated?

Thanks in advance for the update and for keeping our communities secure!
 
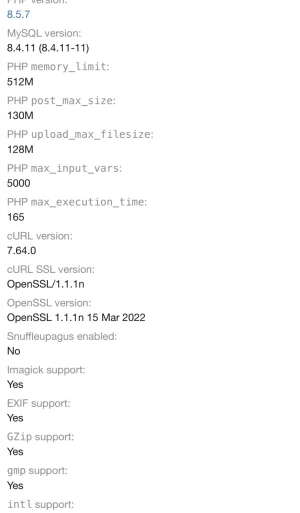
regarding cloud sites: looking for extra guidance on "All XenForo Cloud installations are currently in the process of being patched. You can check whether your installation has been updated by looking at the "Server environment report" block on the Admin control panel index."

I don't see this Server Environment Report and I'm sure that I'm looking in the wrong place
 
Just your forum admin control panel, yes, admin.php. If you don't see it, don't worry about it. The rollout is complete. Perhaps you're logging in with an admin account that doesn't have permission to see it.
 
Looks like my hosting doesn’t have that version yet.
I'd check if the hoster has a status page. In most cases, critical updates (or the plans for those) may be mentioned there. If not I'd shoot them a message. Hard to imagine that a hosting company would not be busy today with updating PHP. Wider parts of the web have been defunct today b/c admins disabled functionality of PHP in expectation of the fix.
 
I'd check if the hoster has a status page. In most cases, critical updates (or the plans for those) may be mentioned there. If not I'd shoot them a message. Hard to imagine that a hosting company would not be busy today with updating PHP. Wider parts of the web have been defunct today b/c admins disabled functionality of PHP in expectation of the fix.

I already sent them an email. Waiting for reply. It’s big hosting company, I would be surprised if they aren’t working on it.
 
I already sent them an email. Waiting for reply.
They may be too busy to reply.
I would be surprised if they aren’t working on it.
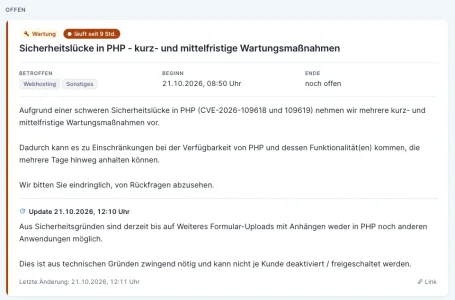
My hoster is a smaller company, they are working on it and say it may in the worst case need a couple of days. Sadly. They have for the meantime crippled the current PHP functionality, so I can't even post an explanation on the forum.
 
They may be too busy to reply.

My hoster is a smaller company, they are working on it and say it may in the worst case need a couple of days. Sadly. They have for the meantime crippled the current PHP functionality, so I can't even post an explanation on the forum.
Time to move. A host worth your money would be all over this issue.
 
Looks like Centminmod has gotten their stuff backported already based on this commit seen just a bit ago.

Code:
commit 691534f46ce0324bc3b32e1c4dd86f287b068cde
Author: George Liu (eva2000) <centminmod@users.noreply.github.com>
Date:   Thu Oct 22 00:28:03 2026 +1000

    backport PHP 8.2.35 security fixes to PHP 7.4-8.1 EOL in 140.00beta01
    
    Backport the fix for CVE-2026-109618 and CVE-2026-109619 (critical, unauthenticated RCE), released in PHP 8.2.35, 8.3.36, 8.4.27 and 8.5.12, to EOL PHP 7.4, 8.0 and 8.1. It is the P
    
    Changes:
    - patches/php: add php742-7.4-cve-2026-109618.patch, php80-8.0-cve-2026-109618.patch and php81-8.1-cve-2026-109618.patch (GHSA-w8hw-w9fx-j79w RCE via OOM corruption, GHSA-6wmf-4rv5-
    - inc/php_patch.inc: append 7.4-cve-2026-109618, 8.0-cve-2026-109618 and 8.1-cve-2026-109618 to the PHP 7.4, 8.0 and 8.1 lists
    - inc/php_patch.inc: for PHP 8.1, touch the generated Zend VM files after patching so make keeps the patched zend_vm_execute.h instead of rerunning zend_vm_gen.php with the installe
    - installer82.sh: PHPVERLATEST fallback 8.2.34 to 8.2.35
    - installer83.sh: PHPVERLATEST fallback 8.3.35 to 8.3.36
    - installer84.sh: PHPVERLATEST fallback 8.4.26 to 8.4.27
    - installer85.sh: PHPVERLATEST fallback 8.5.11 to 8.5.12

 centmin-cli.sh                               |    2 +-
 centmin.sh                                   |    2 +-
 inc/php_patch.inc                            |   12 +-
 installer82.sh                               |    6 +-
 installer83.sh                               |    6 +-
 installer84.sh                               |    6 +-
 installer85.sh                               |    6 +-
 patches/php/php742-7.4-cve-2026-109618.patch |  937 ++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
 patches/php/php80-8.0-cve-2026-109618.patch  |  945 +++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
 patches/php/php81-8.1-cve-2026-109618.patch  | 1180 +++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
 10 files changed, 3085 insertions(+), 17 deletions(-)
 
Time to move. A host worth your money would be all over this issue.
bs. The hosting company IS all over the issue. They started this morning with limiting PHP functionality for security reasons and are thus probably better than many others. Now they are rolling out the updated versions. I don't know how they do this and therefore cannot judge how long it will take. Obviously, updating a compelete hosting environment with tens of thousands of customers is a little bit more complex than updating a single VPS. The patch has now been available for just 2 hours - a bit weird to start complaining already und to suggest searching for a new hoster....

They wrote this morning it may take a couple of days at worst but at this time they had no information yet about what the patches would contain.

Bildschirmfoto 2026-10-21 um 17.51.42.webp

Thousands of websites, even of big corporations and institutions, have been taken completely offline today due to these vulnerabilities and most are not yet back up again.
 
Last edited:
Back
Top Bottom