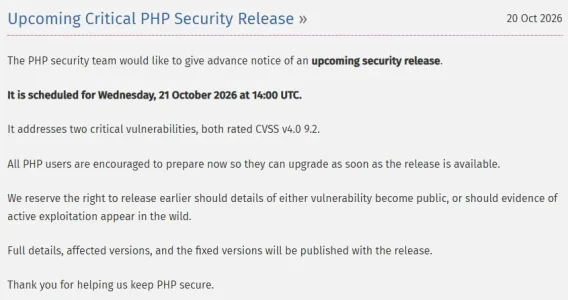
Be prepared to update your PHP tomorrow as there'll be a patch for a 10.0 level CVE tomorrow. PHP.net is not releasing details until then.
php.net is intermittently not responding so here is a screenshot of their latest message.
Proof of concept attack:
https://jackalsyn.com/posts/php-up-2026.html
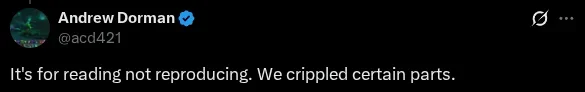
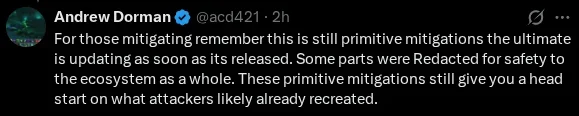
I contacted the authors of this PoC on X and they tell me it's purposefully crippled.
However the mitigation advice looks good
Here's how you'd apply those mitigations:
Please note, the multipart/form-data will very likely break xenforo, i have not tested it. I saw it break the wordpress backend but not the frontend. I'm going through and remediating all servers tonight.
php.net is intermittently not responding so here is a screenshot of their latest message.
Proof of concept attack:
https://jackalsyn.com/posts/php-up-2026.html
I contacted the authors of this PoC on X and they tell me it's purposefully crippled.
However the mitigation advice looks good
Here's how you'd apply those mitigations:
Code:
Add 2 Apache site entry:
# CVE remediation
RewriteEngine On
RewriteCond %{HTTP:Content-Type} ^multipart/form-data [NC]
RewriteRule ^ - [F,L]

Add 2 Nginx site entry:
if ($http_content_type ~* "multipart/form-data") {
    return 403;
}

php.ini:
;CVE mitigation
session.upload_progress.enabled = Off
Please note, the multipart/form-data will very likely break xenforo, i have not tested it. I saw it break the wordpress backend but not the frontend. I'm going through and remediating all servers tonight.