Crazy amount of guests

I actually just switched my main forum back to centminmod server, just the forum on it, all the business sites I manage are now in CF workers/pages, on the edge, a slow process of getting them away from another piece of hardware. It seems with a new IP they all came looking. Funnily enough, I also added my first CF rule back to see how it would go. Good timing.
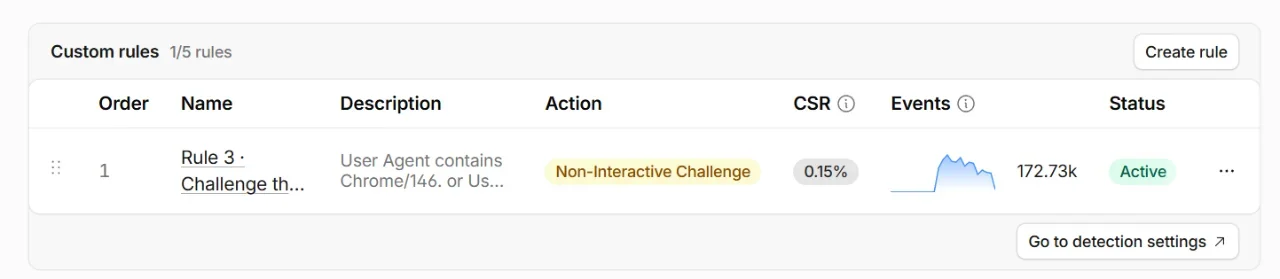
Screenshot 2026-07-22 080941.webp

You can see I flicked that on last night before quitting for the night after setting up the new server and migration, tuning, etc. What I implemented was this one from my heuristics software, which is the real problem child as I see it, bots faking to be humans:

Rule 3 · Challenge the rotating-proxy scraper networks​

Your biggest problem: scraper networks using millions of home IP addresses, 1–2 requests each, disguised as normal browsers. Their weakness: they claim OUTDATED browser versions. Your real visitors run current browsers (Chrome 147–149 right now); these networks claim versions months or years old. This rule gives an invisible browser check to outdated-version visitors arriving with no referrer. Bots fail it; a real person on an old browser passes without noticing. Logged-in members are exempt entirely.
  • 899 stealth campaigns using 8,906,015 IPs made 12,804,480 requests in your data.
  • Versions this rule covers (all heavily used by the networks, barely used by your real visitors): Chrome 146, Chrome 133, Chrome 145, Firefox 135, Firefox 133, Chrome 131, Chrome 116, Chrome 124, Chrome 107, Chrome 104, Chrome 110, Chrome 99…
  • Traffic covered: about 10,357,845 requests.
False-positive risk (low): Roughly 2,332 requests from possible real people on outdated browsers would see the automatic check (0.02% of what the rule catches). They see a brief 'checking your browser' page, not a block, and logged-in members never see it at all.

Code:
(http.user_agent contains "Chrome/146." or http.user_agent contains "Chrome/133." or http.user_agent contains "Chrome/145." or http.user_agent contains "Firefox/135." or http.user_agent contains "Firefox/133." or http.user_agent contains "Chrome/131." or http.user_agent contains "Chrome/116." or http.user_agent contains "Chrome/124." or http.user_agent contains "Chrome/107." or http.user_agent contains "Chrome/104." or http.user_agent contains "Chrome/110." or http.user_agent contains "Chrome/99." or http.user_agent contains "Chrome/119." or http.user_agent contains "Chrome/136." or http.user_agent contains "Chrome/123." or http.user_agent contains "Chrome/100." or http.user_agent contains "Chrome/101." or http.user_agent contains "Chrome/65." or http.user_agent contains "Chrome/108." or http.user_agent contains "Chrome/112." or http.user_agent contains "Chrome/109." or http.user_agent contains "Chrome/103." or http.user_agent contains "Chrome/106." or http.user_agent contains "Chrome/111." or http.user_agent contains "Chrome/105." or http.user_agent contains "Chrome/117." or http.user_agent contains "Firefox/115." or http.user_agent contains "Chrome/135.") and http.referer eq "" and (not cf.client.bot) and (not http.cookie contains "xf_user")

The solved so far, 258 from 172.73k. Those 258 got no CF managed challenge, nothing, they just passed right through. That is a fairly successful rule I would say, and not even a full 24hrs of it. I got hit by a bit over 400k last night, and that one rule took out 40% of it.

I can see addons have a place for people who don't manage their own VPS, but for everyone who does have root access to their server, addons are the to late option IMO.

You don't need to chase IP's or ASN's, even countries, its just not needed.

I still have bot fight mode off, AI Labyrinth off, all bots not trying to fake being a person, are allowed access still. Obviously if you want to get rid of them, use CF and turn those settings on, along with AI bot blocking, then my heuristics show me a rule applicable to my site that you could add if you want to take out the majority of the nasties, as above, non-interactive challenge.

Code:
(http.user_agent contains "ClaudeBot" or http.user_agent contains "Amazonbot" or http.user_agent contains "meta-externalagent" or http.user_agent contains "SemrushBot" or http.user_agent contains "Bytespider" or http.user_agent contains "GPTBot" or http.user_agent contains "AhrefsBot" or http.user_agent contains "DotBot" or http.user_agent contains "ShapBot" or http.user_agent contains "MJ12bot" or http.user_agent contains "AcademicBot" or http.user_agent contains "meta-webindexer" or http.user_agent contains "OAI-SearchBot" or http.user_agent contains "Claude-SearchBot" or http.user_agent contains "yacybot" or http.user_agent contains "PerplexityBot" or http.user_agent contains "compatible; crawler)" or http.user_agent contains "LinkupBot" or http.user_agent contains "Scrapy" or http.user_agent contains "curl" or http.user_agent contains "Turnitin" or http.user_agent contains "ClueWeb-Crawler" or http.user_agent contains "PurityBot" or http.user_agent contains "ImageBot" or http.user_agent contains "Go-http-client" or http.user_agent contains "YisouSpider" or http.user_agent contains "quillbot" or http.user_agent contains "AwarioBot" or http.user_agent contains "IbouBot" or http.user_agent contains "serpstatbot" or http.user_agent contains "CCBot")

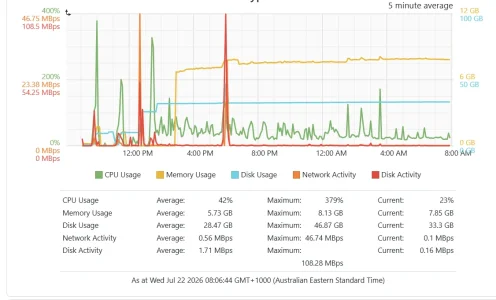
I still have some tuning to do, but with a 400k+ hit overnight, my server didn't blink. I tuned it roughly at setup from past experience, but I have not fine tuned it yet as I don't have the data from it until a few days. That last peak was me testing my backup script, sending them to S3 and then deleting them off the server, then it was all normal. That 400k hit during those small CPU peaks, barely got the server excited.

IMHO, tuning and DNS firewall is the best solution to this problem, albeit for those who can't do either for whatever reasons. Even downgraded specs, 4 cores 12G ram now, from 6 and 16. Once I fine tune from 48+hrs of data, I will throw some traffic at it to see how it goes.
Screenshot 2026-07-22 083307.webp
 
I actually just switched my main forum back to centminmod server, just the forum on it, all the business sites I manage are now in CF workers/pages, on the edge, a slow process of getting them away from another piece of hardware. It seems with a new IP they all came looking. Funnily enough, I also added my first CF rule back to see how it would go. Good timing.

View attachment 341691

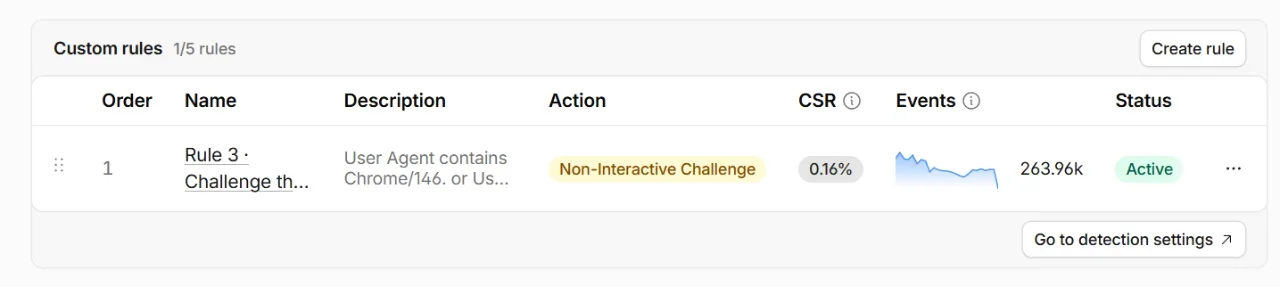
You can see I flicked that on last night before quitting for the night after setting up the new server and migration, tuning, etc. What I implemented was this one from my heuristics software, which is the real problem child as I see it, bots faking to be humans:

Rule 3 · Challenge the rotating-proxy scraper networks​

Your biggest problem: scraper networks using millions of home IP addresses, 1–2 requests each, disguised as normal browsers. Their weakness: they claim OUTDATED browser versions. Your real visitors run current browsers (Chrome 147–149 right now); these networks claim versions months or years old. This rule gives an invisible browser check to outdated-version visitors arriving with no referrer. Bots fail it; a real person on an old browser passes without noticing. Logged-in members are exempt entirely.
  • 899 stealth campaigns using 8,906,015 IPs made 12,804,480 requests in your data.
  • Versions this rule covers (all heavily used by the networks, barely used by your real visitors): Chrome 146, Chrome 133, Chrome 145, Firefox 135, Firefox 133, Chrome 131, Chrome 116, Chrome 124, Chrome 107, Chrome 104, Chrome 110, Chrome 99…
  • Traffic covered: about 10,357,845 requests.
False-positive risk (low): Roughly 2,332 requests from possible real people on outdated browsers would see the automatic check (0.02% of what the rule catches). They see a brief 'checking your browser' page, not a block, and logged-in members never see it at all.

Code:
(http.user_agent contains "Chrome/146." or http.user_agent contains "Chrome/133." or http.user_agent contains "Chrome/145." or http.user_agent contains "Firefox/135." or http.user_agent contains "Firefox/133." or http.user_agent contains "Chrome/131." or http.user_agent contains "Chrome/116." or http.user_agent contains "Chrome/124." or http.user_agent contains "Chrome/107." or http.user_agent contains "Chrome/104." or http.user_agent contains "Chrome/110." or http.user_agent contains "Chrome/99." or http.user_agent contains "Chrome/119." or http.user_agent contains "Chrome/136." or http.user_agent contains "Chrome/123." or http.user_agent contains "Chrome/100." or http.user_agent contains "Chrome/101." or http.user_agent contains "Chrome/65." or http.user_agent contains "Chrome/108." or http.user_agent contains "Chrome/112." or http.user_agent contains "Chrome/109." or http.user_agent contains "Chrome/103." or http.user_agent contains "Chrome/106." or http.user_agent contains "Chrome/111." or http.user_agent contains "Chrome/105." or http.user_agent contains "Chrome/117." or http.user_agent contains "Firefox/115." or http.user_agent contains "Chrome/135.") and http.referer eq "" and (not cf.client.bot) and (not http.cookie contains "xf_user")

The solved so far, 258 from 172.73k. Those 258 got no CF managed challenge, nothing, they just passed right through. That is a fairly successful rule I would say, and not even a full 24hrs of it. I got hit by a bit over 400k last night, and that one rule took out 40% of it.

I can see addons have a place for people who don't manage their own VPS, but for everyone who does have root access to their server, addons are the to late option IMO.

You don't need to chase IP's or ASN's, even countries, its just not needed.

I still have bot fight mode off, AI Labyrinth off, all bots not trying to fake being a person, are allowed access still. Obviously if you want to get rid of them, use CF and turn those settings on, along with AI bot blocking, then my heuristics show me a rule applicable to my site that you could add if you want to take out the majority of the nasties, as above, non-interactive challenge.

Code:
(http.user_agent contains "ClaudeBot" or http.user_agent contains "Amazonbot" or http.user_agent contains "meta-externalagent" or http.user_agent contains "SemrushBot" or http.user_agent contains "Bytespider" or http.user_agent contains "GPTBot" or http.user_agent contains "AhrefsBot" or http.user_agent contains "DotBot" or http.user_agent contains "ShapBot" or http.user_agent contains "MJ12bot" or http.user_agent contains "AcademicBot" or http.user_agent contains "meta-webindexer" or http.user_agent contains "OAI-SearchBot" or http.user_agent contains "Claude-SearchBot" or http.user_agent contains "yacybot" or http.user_agent contains "PerplexityBot" or http.user_agent contains "compatible; crawler)" or http.user_agent contains "LinkupBot" or http.user_agent contains "Scrapy" or http.user_agent contains "curl" or http.user_agent contains "Turnitin" or http.user_agent contains "ClueWeb-Crawler" or http.user_agent contains "PurityBot" or http.user_agent contains "ImageBot" or http.user_agent contains "Go-http-client" or http.user_agent contains "YisouSpider" or http.user_agent contains "quillbot" or http.user_agent contains "AwarioBot" or http.user_agent contains "IbouBot" or http.user_agent contains "serpstatbot" or http.user_agent contains "CCBot")

I still have some tuning to do, but with a 400k+ hit overnight, my server didn't blink. I tuned it roughly at setup from past experience, but I have not fine tuned it yet as I don't have the data from it until a few days. That last peak was me testing my backup script, sending them to S3 and then deleting them off the server, then it was all normal. That 400k hit during those small CPU peaks, barely got the server excited.

IMHO, tuning and DNS firewall is the best solution to this problem, albeit for those who can't do either for whatever reasons. Even downgraded specs, 4 cores 12G ram now, from 6 and 16. Once I fine tune from 48+hrs of data, I will throw some traffic at it to see how it goes.
View attachment 341692
Implemented this, thank you!

Now if only I could exclude logged in users based on cookie for my rate limiting rule, but that's Enterprise plan only.. 🥲
 
So yeah.
I'm working on two things for cloudflare:
1. UAM auto-switch flipper ( recently revised, and testing in audit mode for a few days, will deploy; will publish when i have results )
2. Fail2ban -> cloudflare integration

Why #2?
Cloudflare limits the amount and complexity of rules that can be applied with lower cost plans.
There is already an established way to have cloudflare controlled by fail2ban ( both banning and unbanning functions ).
We should be able to get better protection for cheaper. :)

Let me know if there is a hole in my plan.

I will be moving our Xenforo forum over to hybrid cloudflare/fail2ban as an interim option while i'm building v2 of my security system.
 
Fail2ban -> cloudflare integration
Interesting. I guess you could do this with any firewall really. Log your blocked IP's to a custom list (fw_blocklist), write a little script, token into the CF account > Account Filter Lists > Edit, and write a custom WAF expression, (ip.src in $fw_blocklist), set it to block or challenge, then use an action that POSTs/DELETEs via the Lists API.

CSF's lfd does layer 7 login-failure banning with CF support. Just discovered that one after researching this idea. Not that it serves much purpose for bots scraping... but I learnt something new.

Keeps it all in one rule, nice and simple, and available to all on the Free Plan, just auto-updates and keeps the nasties away without hitting limits or restrictions on CF.

I would love to have something similar to my desktop heuristics software on the server, where its auto updating a CF ruleset from constant log analysis... but I know it would cripple a small VPS holding and analysing that level of logs.
 
Last edited:
What is 'CSF's lfd'?

Recommended practice is to have one giant list for fail2ban, which it maintains the blocks and unblocks. From there you can challenge.

We're just completing a library that uses proxycheck.io single or batch query mode. Once i have that, i plan to write a cronjob which looks up every unique IP's ASN ( among other data ) and produce a report of what ASNs are the most active over the last 24h.
You could do a lot of interesting things with that report with additional code. Like email you a report or automatically ban if we see X hits/day from any ASN.

Results from proxycheck.io will be cached for a week ( you can set it longer ) to reduce cost of running the API.
Some additional logic could be added to skip lookups using our existing list of ASNs and IP ranges.

Coming toon to a fine open source repository near you.
 
login failure daemon is its watcher, logs and triggers. Argh... proxycheck. Don't get me wrong, its amazing at what it does, but for large sites, it just becomes another expense, and it gets expensive fast on heavy trafficked sites.

It is far cheaper for me to have more cpu and ram, combined with well tuned, to manage traffic, than it was an addon using proxycheck to check every IP.
 
I had this one persistent spammer using the guest post system just recently. They started at one, ended up at around 25+ daily, all going into moderation with the default XF system, but its just annoying behaviour. Finally got the time to track them through the logs today, pattern recognition, isolated it down to about 70, then got it nailed to the exact amount since last night.

FAKE 23/Jul/2026:00:58:43 +1000 145.223.58.239 US
FAKE 23/Jul/2026:01:20:37 +1000 103.75.228.80 BE
FAKE 23/Jul/2026:01:26:32 +1000 146.103.3.16 GB
FAKE 23/Jul/2026:01:30:16 +1000 62.105.202.39 BE
FAKE 23/Jul/2026:02:54:29 +1000 45.151.163.107 DE
FAKE 23/Jul/2026:03:16:37 +1000 82.23.223.251 FR
FAKE 23/Jul/2026:03:22:48 +1000 92.113.242.243 ES
FAKE 23/Jul/2026:03:26:43 +1000 31.58.29.200 US
FAKE 23/Jul/2026:04:51:37 +1000 38.154.227.102 US
FAKE 23/Jul/2026:05:12:33 +1000 154.6.83.96 US
FAKE 23/Jul/2026:05:17:59 +1000 168.199.244.219 NL
FAKE 23/Jul/2026:05:21:23 +1000 217.198.177.244 IT
FAKE 23/Jul/2026:05:39:23 +1000 5.196.78.175 FR
FAKE 23/Jul/2026:06:40:04 +1000 45.43.64.190 GB
FAKE 23/Jul/2026:07:05:52 +1000 104.239.42.180 CA
FAKE 23/Jul/2026:07:11:27 +1000 64.137.58.32 IT
FAKE 23/Jul/2026:07:15:01 +1000 172.102.222.157 FI
FAKE 23/Jul/2026:08:35:52 +1000 45.83.57.217 IT
FAKE 23/Jul/2026:08:56:38 +1000 64.137.49.170 FR
FAKE 23/Jul/2026:09:02:22 +1000 104.239.17.97 IT
FAKE 23/Jul/2026:09:05:58 +1000 166.88.235.190 US
FAKE 23/Jul/2026:10:19:15 +1000 195.2.84.198 RU
FAKE 23/Jul/2026:10:27:03 +1000 92.112.217.145 SE
FAKE 23/Jul/2026:10:51:24 +1000 178.20.45.159 RU
FAKE 23/Jul/2026:10:53:54 +1000 104.143.245.230 ES
FAKE 23/Jul/2026:10:58:57 +1000 31.57.88.90 DE
FAKE 23/Jul/2026:11:02:29 +1000 104.253.36.111 CA

No amount of IP or ASN blocking can deal with that. One rule, either new or an OR in existing rules, fixed them up. Just confirmed it captured them on a managed challenge.

Code:
(http.request.method eq "POST"
 and http.request.uri.path contains "/post-thread"
 and http.user_agent contains "Chrome/1"
 and not any(lower(http.request.headers["accept"][*])[*] contains "avif"))
 
What is 'CSF's lfd'?

Recommended practice is to have one giant list for fail2ban, which it maintains the blocks and unblocks. From there you can challenge.

We're just completing a library that uses proxycheck.io single or batch query mode. Once i have that, i plan to write a cronjob which looks up every unique IP's ASN ( among other data ) and produce a report of what ASNs are the most active over the last 24h.
You could do a lot of interesting things with that report with additional code. Like email you a report or automatically ban if we see X hits/day from any ASN.

Results from proxycheck.io will be cached for a week ( you can set it longer ) to reduce cost of running the API.
Some additional logic could be added to skip lookups using our existing list of ASNs and IP ranges.

Coming toon to a fine open source repository near you.
https://github.com/Aetherinox/csf-firewall - predates Cloudflare by a long-shot. Installable to just about any modern linux flavor operating system. When configured to operate in cluster mode, along with some additional upstream (and downstream) configurations, it's incredibly powerful. CSF does utilize blocklists, and are pulled and cached based on the duration the server admin has set.

Problem is this: it scales poorly under moderate to extreme loads. The LFD's min check time is 5 seconds between log file parses, and it only checks up to 5000 lines at any given time to each log file scanned. High to huge activity servers will easily overwhelm this periodic check. It is one of the largest weaknesses of CSF, since it doesn't support real-time log streaming.

CSF can also send temp and perma ban notifications to a central location outside of CSF, but that does require the use of some bash (or otherwise native installed language on the OS) scripting to perform said task. The Cloudflare integration is a native addition, but I've rarely kicked on that feature.
 
I had this one persistent spammer using the guest post system just recently. They started at one, ended up at around 25+ daily, all going into moderation with the default XF system, but its just annoying behaviour. Finally got the time to track them through the logs today, pattern recognition, isolated it down to about 70, then got it nailed to the exact amount since last night.

FAKE 23/Jul/2026:00:58:43 +1000 145.223.58.239 US
FAKE 23/Jul/2026:01:20:37 +1000 103.75.228.80 BE
FAKE 23/Jul/2026:01:26:32 +1000 146.103.3.16 GB
FAKE 23/Jul/2026:01:30:16 +1000 62.105.202.39 BE
FAKE 23/Jul/2026:02:54:29 +1000 45.151.163.107 DE
FAKE 23/Jul/2026:03:16:37 +1000 82.23.223.251 FR
FAKE 23/Jul/2026:03:22:48 +1000 92.113.242.243 ES
FAKE 23/Jul/2026:03:26:43 +1000 31.58.29.200 US
FAKE 23/Jul/2026:04:51:37 +1000 38.154.227.102 US
FAKE 23/Jul/2026:05:12:33 +1000 154.6.83.96 US
FAKE 23/Jul/2026:05:17:59 +1000 168.199.244.219 NL
FAKE 23/Jul/2026:05:21:23 +1000 217.198.177.244 IT
FAKE 23/Jul/2026:05:39:23 +1000 5.196.78.175 FR
FAKE 23/Jul/2026:06:40:04 +1000 45.43.64.190 GB
FAKE 23/Jul/2026:07:05:52 +1000 104.239.42.180 CA
FAKE 23/Jul/2026:07:11:27 +1000 64.137.58.32 IT
FAKE 23/Jul/2026:07:15:01 +1000 172.102.222.157 FI
FAKE 23/Jul/2026:08:35:52 +1000 45.83.57.217 IT
FAKE 23/Jul/2026:08:56:38 +1000 64.137.49.170 FR
FAKE 23/Jul/2026:09:02:22 +1000 104.239.17.97 IT
FAKE 23/Jul/2026:09:05:58 +1000 166.88.235.190 US
FAKE 23/Jul/2026:10:19:15 +1000 195.2.84.198 RU
FAKE 23/Jul/2026:10:27:03 +1000 92.112.217.145 SE
FAKE 23/Jul/2026:10:51:24 +1000 178.20.45.159 RU
FAKE 23/Jul/2026:10:53:54 +1000 104.143.245.230 ES
FAKE 23/Jul/2026:10:58:57 +1000 31.57.88.90 DE
FAKE 23/Jul/2026:11:02:29 +1000 104.253.36.111 CA

No amount of IP or ASN blocking can deal with that. One rule, either new or an OR in existing rules, fixed them up. Just confirmed it captured them on a managed challenge.

Code:
(http.request.method eq "POST"
 and http.request.uri.path contains "/post-thread"
 and http.user_agent contains "Chrome/1"
 and not any(lower(http.request.headers["accept"][*])[*] contains "avif"))
The odds are good that the Spaminator add-ons would have stopped these before they happened.
 
The odds are good that the Spaminator add-ons would have stopped these before they happened.
Some, yes... some, no. Some are VPN, some are Proxies, some are residential, corporate, there was a good mix. The above is just some of it, there was more, and I scanned all the IP's to see if something that easy could solve it. Unfortunately, they still would have partially gotten through. Now... zero.

Saying that, none of this went live, because default XF allows me to capture anything with a link in new posts for guests or new members. I just wanted to stop the annoyance of the deleted content.

You can pretty much have the one managed challenge rule in CF, just keep adding OR logic, as its highly unlikely that two expressions meet at the exact same second being scanned, so one rule should easily do the job to block bad actors at DNS, not the server. I also acknowledge and understand that for some, its just easier or the only option, to use an addon.

The addons come with a cost that I am happy to avoid. They either load the server or they cost $$$ for a busy site. Good for small traffic sites, absolutely. OH... and they can also block legitimate relevant discussion from a passer-by.
 
Some, yes... some, no. Some are VPN, some are Proxies, some are residential, corporate, there was a good mix. The above is just some of it, there was more, and I scanned all the IP's to see if something that easy could solve it. Unfortunately, they still would have partially gotten through. Now... zero.
The Spaminator does not look at or care about the source of the traffic.

It creates random fields for registration, login and contact forms that only a bot would see and fill in. These look like fields some forums set up as required, and the bots fill them in. When they do, it doesn't give them an error message but lets them blindly think they succeeded when they haven't.

They have no added load, since they only run when the form is presented and submitted. Bots have been developed to deal with widely used anti-bot tactics such as Cloudflare's challenges, not an add-on with such a small audience.

It sounds like you are thinking of it like other anti-bot add-ons, when it deals with spam in an entirely different way. It also doesn't cost anything other than the initial license, which is not tied to forum size.

"There is a principle which is a bar against all information, which is proof against all arguments and which can not fail to keep a man in everlasting ignorance - that principle is contempt prior to investigation." Herbert Spencer
 
Last edited:
It sounds like you are thinking of it like other anti-bot add-ons, when it deals with spam in an entirely different way.
Also, spambots are not really the topic of this thread - it is a way different issue, but rarely, as per the issues discussed in this thread, hundreds, thousands, ten thousands or hundreds of thousands in parallel.

Some may use the same infrastructure as other bots, but in to be able to spam they must register first and this where add ons like spaminator or "Signup abuse detection and blocking" come to the rescue. Completely different world from scraping bots.

Their complaint was "I had this one persistent spammer using the guest post system just recently" and my post was clearly a response to that specific problem.

Thanks for paying attention. :-)

GIF by Next Level Chef
 
I had this one persistent spammer using the guest post system just recently.

Their complaint was "I had this one persistent spammer using the guest post system just recently" and my post was clearly a response to that specific problem.
Wasn't meant to criticize you. ;) But if we start to talk about each and every issue with visitors on our forums the thread probably loses its focus quickly.:cool:

PS: Would Spaminator really help against Guest Posting? Never enabled that (for obvious reasons as I dislike spam) but had assumed that one could post w/o registration then and in this case the Registration Spaminator would and could do nothing.
 
Argh... proxycheck. Don't get me wrong, its amazing at what it does, but for large sites, it just becomes another expense, and it gets expensive fast on heavy trafficked sites.
...
It is far cheaper for me to have more cpu and ram, combined with well tuned, to manage traffic, than it was an addon using proxycheck to check every IP.

I'm surprised by that. Proxycheck is pretty cheap. You must have a way better deal on hosting than i do 😅

1784906154488.webp

Right now, i'm setting up a centralized server for it so that my 35 servers can pull cached results from it.
Also, my protection mechanism keeps an IP state table in memory at all times, so it only needs to query our central server once every 7 days.

Some investment is needed but it is possible to use this at scale inexpensively.
You just need to proxy your proxycheck.. 😅
 
Speaking of proxies;
https://krebsonsecurity.com/2026/07/lg-to-ban-residential-proxies-from-smart-tv-apps/

The home appliance giant LG Electronics USA said this week it plans to suspend any apps built for its smart TVs that turn one’s television into an always-on residential proxy node. The move comes less than a month after researchers found that more than 42 percent of games and other apps available for download on LG’s webOS store allow unknown third-parties to route their Internet traffic through a user’s TV.
 
Wasn't meant to criticize you. ;) But if we start to talk about each and every issue with visitors on our forums the thread probably loses its focus quickly.:cool:
No worries. I responded because I believe this is in the realm of discouraging bots overall.

Though posting bots don't use up bandwidth and server resources like AI crawlers do, they do consume human resources to moderate them. I've seen some of these bots check back later to find their post. I assume if they do, then the site will end up on a list of sites vulnerable to spam, resulting in more spam.

PS: Would Spaminator really help against Guest Posting? Never enabled that (for obvious reasons as I dislike spam) but had assumed that one could post w/o registration then and in this case the Registration Spaminator would and could do nothing.
I have "Enable writing before registering" enabled, and it stops them.

After hitting submit on the post, they are given the registration screen. The post isn't even in the moderation queue because it doesn't have a valid user to attach to. Xenforo holds it in a pending post queue, waiting up to 24 hours to expire it if the same post session doesn't successfully register.

It's rare for my XF 2 sites to get guest post spam. :-)
 
Back
Top Bottom