Crazy amount of guests

but my bet, is that over time, they will be back with a different user agent string
100% agree. This is why this will change month to month, it updates for me monthly when I feed it the previous months logs. It looks at new patterns, old patterns, what is used now, what is not, etc etc etc. For me, it will be an automated monthly update of the rule via API. I am just sharing that rule for others to help with the residential proxy issue at DNS, so it lessens the issue at the server.

I would also probably make the rule, unmanaged challenge, IF you have a higher percentage of solves, letting CF do its thing without showing a captcha to the user.
 
Yeah. I'd definitely not use user agents. if someone happens to be using that version of a browser, they'll have a bad time on your site. Also, these versions numbers are going to be constantly changing over time, so it's hard to keep up with them. The false positive rate will be high.

A web server log is close to useless as a way to find bots today :/
 
A web server log is close to useless as a way to find bots today
Yet implementing a heuristics algorithm... and this is exactly what it can do from pattern recognition, and output a safe CF rule for use that stops the majority, not all, but majority, without affecting members and majority guests. It is exactly applying psychology to a math problem. Everything has a pattern, that is factual, mathematical. Even chaos has a pattern.
 
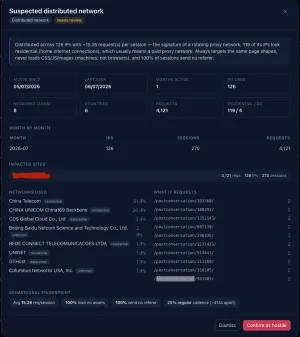
View attachment 341102

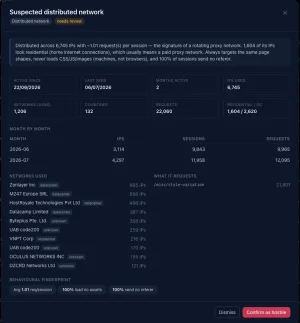
This is what I've started seeing lately sucking up most of the requests to multiple XF sites. The bots are churning through the style-variation URL
Interesting. How did you get that analysis? Seems pretty decent. Haven't seen "Oculus Networks Inc", all the others have been well known annoyances for ages and have been blocked w/o harm already quite a while ago on m site by ASN blocking or - in case of VNPT - country blocking.
 
Possibly a key point to remember is that we're not looking for A solution, a single, magical rule on the receiving end that would identify (and block) bots.

We have to think in layers. Have 5 or 8 or 20 different triage levels for all sorts of criteria, so that every time some of the traffic gets routed out. Lots of other activities follow the same approach: theft deterrent, or water purification, or patient intake.

Then the second step is to put those layers at their right places in the chain so that they are most efficient. You can do with software any kind of fancy stuff, but to do IP level filtering at the endpoint is the most "expensive" way of doing it instead of putting that filtering upstream into the transport layer where dedicated hardware can do it much, much better. I mean, you don't want all sick people entering the hospital door to go all the way to the sterile operating room and get their first check there; there's layers of checks, filters and decisions along the way, and for good reason.

So I tend to agree with the line of thought that XenForo should not step (too much) out of its intended purpose as a web app, and go nuts into becoming a security/privacy tool as well. I would expect that the forum admin buying the solution is given some guidance or best practices or at least some hints into setting up their server so that the forum experience is reasonably good, and that XF does have some built-in features to cater to the different options for every decision a forum admin needs to make. Like, if I want to allow or disallow some types of bots, how do I do that? If I want full, limited or no access for guests, how do I do that? If privacy/GDPR/anonymity is a concern, how do I tackle that? (I still have a GDPR issue with birthdays being stored in the database, for example.) Can I build my wall for the garden as a forum plugin if I want to, or can I use another component lower in the stack on my server or upstream in the communication path, or a combination of them? Do I have any flexibility to decide for myself and combine stuff, or do I absolutely have to fit within the rigid assumptions of the product?

However, although technically XenForo can be developed to incorporate stuff, I don't think it is the right approach for it to turn into a monolithic bundle of forum AND security AND who knows what else we want to throw at it then. Use a combination of different tools that are best for their limited purpose, deployed at the right place in the chain, and together they integrate to fit the need. Layers.

We could go down an endless philosophical debate about responsibility and where it fails in this chain from the forum as the end target and going upstream towards the source of the problem:
  • Should the web application embed security features, or should there be two distinct components in the stack, one for the web app and another for the web app firewall?
  • Should web hosts be responsible for hardening their servers, or why should it be tolerated that people with zero server admin experience or training can just rent VPS and introduce a vulnerable system in the internet?
  • Should datacenters on the hosting side be responsible for ingress filtering and/or a way for customers to control the firewall rules there?
  • Should transit networks have any responsibility in any security monitoring or at least an efficient, automated way for bad traffic to be reported and blocked?
  • Should datacenters hosting bot farms be responsible to monitor their clients' software and use of infrastructure, proactively enforce their ToS and/or laws concerning abuse, and doing client screening before signing them up, and having effective methods to process the feedback that some clients are doing nasty stuff and terminate them (with penalties)?
  • Should the people who buy "smart" devices have to take some training and pass some certification for their explicit responsibility coming with owning an internet-connected device, before they can buy said device?
  • Should manufacturers of "smart" devices have to pass through some security certifications for their firmware and some legal obligations for long term security patching as part of their conformity approval for bringing a new product on the market?
  • Should legislative bodies, governmental agencies and industry regulators do better at establishing and enforcing security and fair use of the internet?
Having just written that, I'm pissed to realize how little control do we actually have, how surprisingly long did the internet function relatively ok on such a rotten foundation, and how easy it is for unscrupulous agents to just do as they please with little to zero consequences.

One more thing, steming from decades of being a little cog in the machinery of Fortune 500 enterprises: whenever you face a crisis or incident, it is important to get onto fixing it, but it is MORE important to communicate about it. For a technically minded person it is f'ing annoying to have to interrupt the work on a fix to join war room calls or send e-mails or notifications about the issue, the progress, the projected road ahead etc. - that's why some companies' major incident management process pair up the technical skilled people with incident managers who only do the communication side of it. There is immense benefit from lots of other people being informed, not just from the problem being fixed.

So kudos to @Chris D for the insane amount of work to stabilize the inflow of traffic abusing the hosted forums infrastructure. We share the pain (possibly not at that level, but this thread is evidence of how many people face the same issues) but I wish we joined forces earlier through open communication and figuring things together. Leverage the power of community facing a common problem, let them pitch in ideas and test things while you get some much needed sleep, then come back in the morning to a maybe half baked thing which might actually work for a while.

Neither of us is alone in this.
 
Last edited:
The bots are churning through the style-variation URL
They did something similar to my forums some weeks ago, but they were all hitting the cookies page (/misc/cookies if I'm not mistaking). All I could figure out at that time is that they were either attempting some brute force of some kind through weird GET parameters (which they did send), or fine tuning the bots and queries against a fairly innocent, publicly facing page with predictably static contents. It is fairly unusual for a human visitor to hit that page directly without going maybe through the front page of the forum or maybe one of the search engine indexed threads, and having no referral URL, so I put a temporary filter for /misc without the proper referral. Crude, but it did the job.

PS: why would guests have permissions to try more styles? Keep that as a feature for registered members, and leave guests just with one default style.
 
Last edited:
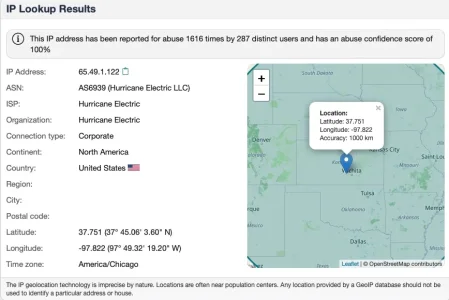
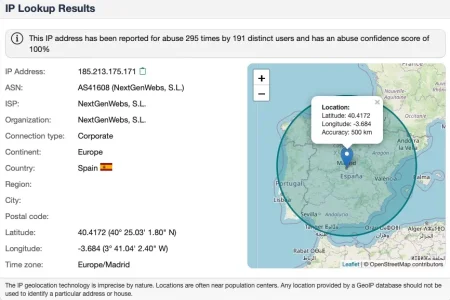
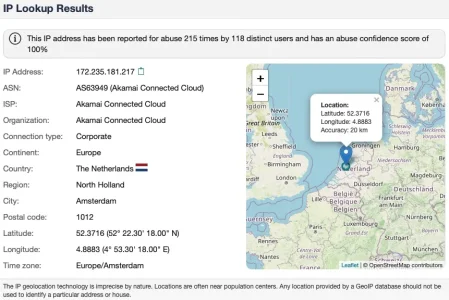
A somewhat amusing sidenote regarding "who are the baddies":

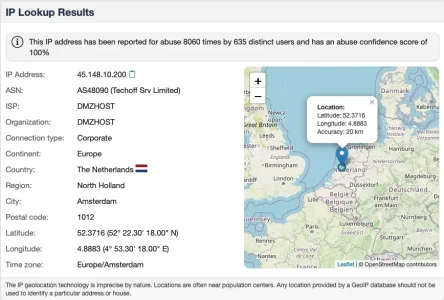
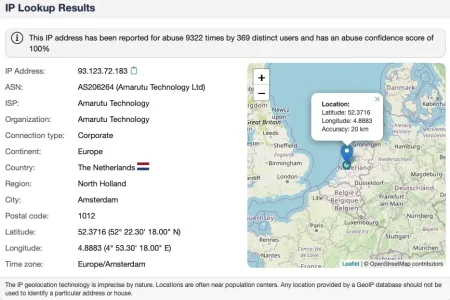
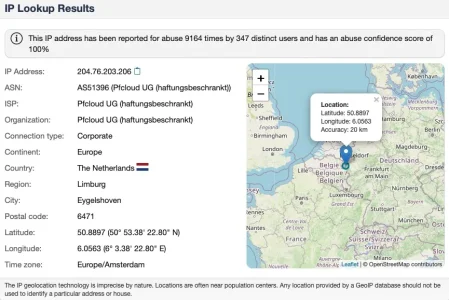
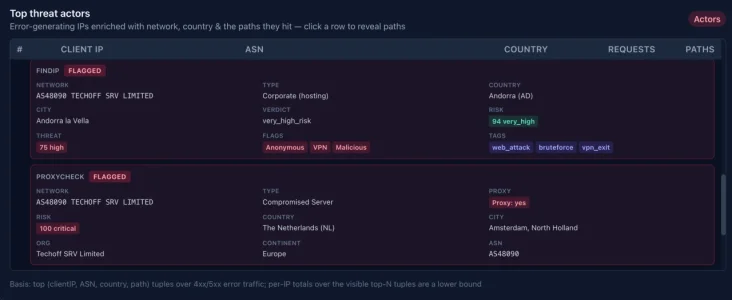
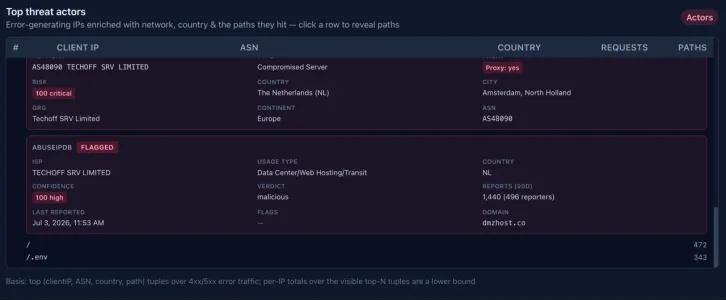
As I'm in the process to prepare a move of my forum to a different setup I've ordered a virtual server a couple of days ago and am in the process of setting it up. It does have a DNS-A record for the host name, but that's about it. No content, no links to it, no nothing - just a brand new, for the most part locked down, empty box running nginx. Yet still there is a reasonable amount of noise in the webserver logs already. So either some simply go through IP ranges or they somehow grab changes in the DNS. Good opportunity to identify some bulletproof providers and networks that are worth locking out. I only checked a couple of the IPs but those draw a pretty clear picture, i.e.:

Bildschirm­foto 2026-07-06 um 09.16.22.webp
Bildschirm­foto 2026-07-06 um 09.17.21.webp
Bildschirm­foto 2026-07-06 um 09.18.26.webpBildschirm­foto 2026-07-06 um 09.19.38.webp
Bildschirm­foto 2026-07-06 um 09.20.48.webpBildschirm­foto 2026-07-06 um 09.34.10.webp
 
A somewhat amusing sidenote regarding "who are the baddies":

As I'm in the process to prepare a move of my forum to a different setup I've ordered a virtual server a couple of days ago and am in the process of setting it up. It does have a DNS-A record for the host name, but that's about it. No content, no links to it, no nothing - just a brand new, for the most part locked down, empty box running nginx. Yet still there is a reasonable amount of noise in the webserver logs already. So either some simply go through IP ranges or they somehow grab changes in the DNS. Good opportunity to identify some bulletproof providers and networks that are worth locking out. I only checked a couple of the IPs but those draw a pretty clear picture, i.e.:
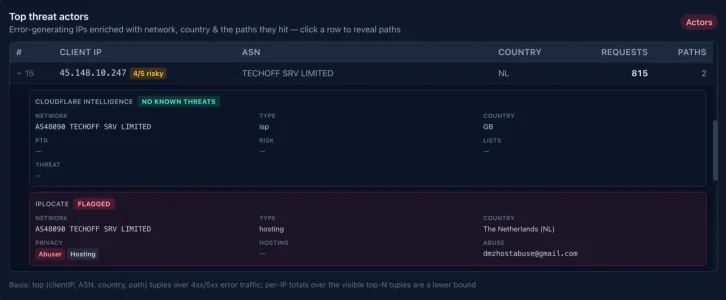
Techoff made my list too 4/5 IP intelligence data sources flagged the ASN IP

1783325272047.webp
1783325297137.webp
1783325331722.webp
 
Interesting. How did you get that analysis? Seems pretty decent. Haven't seen "Oculus Networks Inc", all the others have been well known annoyances for ages and have been blocked w/o harm already quite a while ago on m site by ASN blocking or - in case of VNPT - country blocking.
All my servers ship the logs back to a central rsyslog server, and I've been building something similar to what @Anthony Parsons has built, so I have access to TB's worth of access logs for various different setups (centminmod / nginx / cPanel / DirectAdmin / apache), so I can parse and analyze them all.
 
All my servers ship the logs back to a central rsyslog server
Ah when disk storage was much cheaper! :)

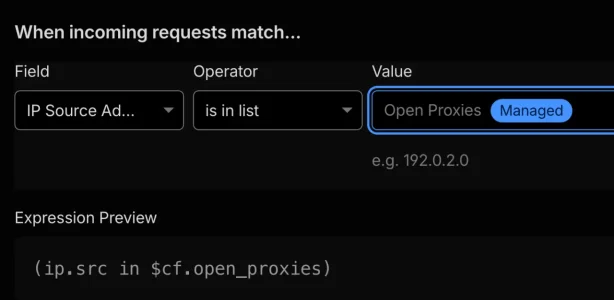
I was going use my aggregated IP intelligence data from IPs to pass back to Cloudflare custom IP list for WAF usage but reminded Cloudflare Enterprise also has premade lists https://developers.cloudflare.com/waf/tools/lists/managed-lists/

Use Managed IP Lists to access Cloudflare's IP threat intelligence.

Cloudflare provides the following Managed IP Lists:

Display nameName in expressionsDescription
Cloudflare Open Proxiescf.open_proxiesIP addresses of known open HTTP and SOCKS proxy endpoints, which are frequently used to launch attacks and hide attackers identity.
Cloudflare Anonymizerscf.anonymizerIP addresses of known anonymizers (Open SOCKS Proxies, VPNs, and TOR nodes).
Cloudflare VPNscf.vpnIP addresses of known VPN servers.
Cloudflare Malwarecf.malwareIP addresses of known sources of malware.
Cloudflare Botnets, Command and Control Serverscf.botnetccIP addresses of known botnet command-and-control servers.

1783327228053.webp

For non-Enterprise plans, you of course can create your own lists ;) I might do both
 
Ah when disk storage was much cheaper! :)
I recently had to purchase 4x8tb nas drives for my SHA setup... $2.5k for disks. WTF! I think it uses 6tb with 15tb free at the moment. Disk prices are not what I experienced a couple years back.

Oh... and that cheap 5090 fell through. Dodgy supplier was exactly that, dodgy. Off to the shop I go.
 
View attachment 341102

This is what I've started seeing lately sucking up most of the requests to multiple XF sites. The bots are churning through the style-variation URL
I've released a new version of my StandardLib add-on which implements a version of the linkpost XF2.4 feature for XF2.1/XF2.2/XF2.3;


I've been considering adding an option to disable the redirect url that is getting added into the url but for now removing the session token should help.
 
So I can just 444 them with nginx
Wouldn't it be easier to just whitelist the friendly URL paths that are expected for XenForo and 444 anything else? The basics for it would already be in .htaccess for mod_rewrite.
 
Back
Top Bottom