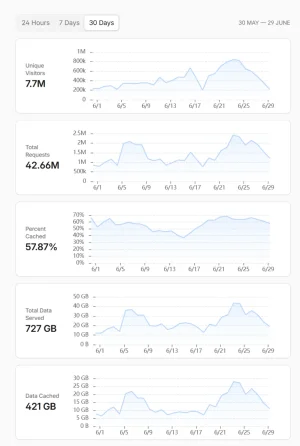
Crazy amount of guests

Personally, I don't have an issue with bot scraping. I don't care what they use it for. If you put it online, publicly available, then its a free for all. If you let Google have it, you may as well let anyone have it, its public after all. If you want private stuff online, then make it private, no such issues with bot scraping.

Saying that... I don't like the intensity, the abusive manner of scraping where it affects and impacts peoples server resources making human visitors interaction poor, slow loading, crashes, etc. I have demonstrated that you can run a multi-million post forum on about $15 a month server, BUT, greedy bots will make human interaction crap because they don't want to limit themselves. Honestly, Microsoft is one of the biggest offenders, Facebook too. Why does Facebook need to aggressively scrape the web to provide social media services? Why are these companies being so aggressive and pissing people off in the process? Why are people just farming for no real intention, other than to be annoying or try and build some personal library for their own experimentation?

A real simple solution would be a global infrastructure limit on all automated detected activity, 1 visit per domain, per 15 seconds. That would come close to solving the entire internet if handled at the tier level infrastructure, anyone not playing fair gets spanked, even those pesky invaders of tv apps using infrastructure unknowingly to most consumers. Big business out there can fingerprint bots, but everyone is charging big bucks for the good stuff, instead of rolling it out freely to actually stop the problem.

It was like using ProxyCheck, I got the impression that the more I queried them, the traffic kept growing, hitting the next limit, requiring upgrade, more $$$. Maybe I'm paranoid... maybe its all a ploy to start paying money for things you don't need, but someone is forcing it upon the web nonetheless. After seeing Anubis in action from @BrettC on my own test server, I think server companies need to be rolling that stuff out network wide, removing the issue from all customers in one swoop.
 
Last edited:
After seeing Anubis in action from @BrettC on my own test server, I think server companies need to be rolling that stuff out network wide, removing the issue from all customers in one swoop.
There's a problem with that though... once Anubis gains enough traction, and once these abusive AI-scraper botnet runners "figure it out", they'll just make their clients wait an extra long time despite the compute power needed. At that point, you're down to two options: 1) Implement exceptionally harsh challenge levels to non-ISP providers on IPv4 and IPv6 (I actually do this to all of the Alibaba, TenCent, and some other abusive AS's out there), 2) up the challenge level across the board, but at the same time alienating guest-users. With #2, you then need to implement whitelists/bypasses for legitimate/auth'd users to your services.

It's a dynamic game of cat n mouse.
 
A real simple solution would be a global infrastructure limit on all automated detected activity
Sounds great, but... how does it detect automated activity? Corporate greed that wants to take everything with absolutely no care about rules or other people's costs will likely continue to invest in dodging rules than playing fair. That's the whole conundrum here: who can effectively define fair use policies and enforce control better than the status quo?
 
Sounds great, but... how does it detect automated activity?
You already have corporations such as the earlier fingerprint.com, Cloudflare Enterprise have exceptional bot recognition. There are plenty of others too... but they all cost considerably, far beyond the normal end user would pay. This ability to identify them already exists... most people just don't have access to it. Look at fingerprint.com, Tiktok use them so their infrastructure isn't affected by all this. But they pay big $$$ for it as special clients. The ability is already there, its just the majority of the web can't afford to access it.
 
Yep... solutions are inequitable due to cost. It's why the open source fight in this space is limited, and important. The hard thing is - corporations pay big dollars for enterprise solutions, but the open source projects are scarcely financially supported. Big corporations offering bot protection products often use / borrow the work of open source projects, too. It is difficult.
 
So it's not really a solution on ALL automated detected activity, it's only for those who can afford it. So much for unity of internet; two classes for the win, those who have the money get protection or preferred treatment, the others can go f themselves. Sorry but this is Animal Farm's "all animals are equal with the others, but some are more equal than others"...
 
You already have corporations such as the earlier fingerprint.com, Cloudflare Enterprise have exceptional bot recognition. There are plenty of others too... but they all cost considerably, far beyond the normal end user would pay. This ability to identify them already exists... most people just don't have access to it. Look at fingerprint.com, Tiktok use them so their infrastructure isn't affected by all this. But they pay big $$$ for it as special clients. The ability is already there, its just the majority of the web can't afford to access it.
I can vouch for Cloudflare Enterprise Bot Management it eats bots and crawlers for breakfast :D

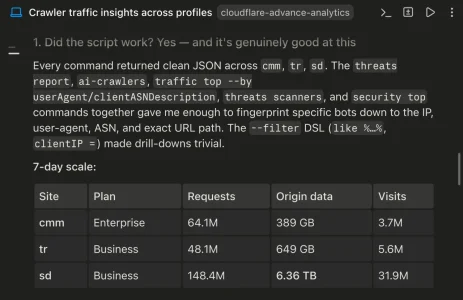
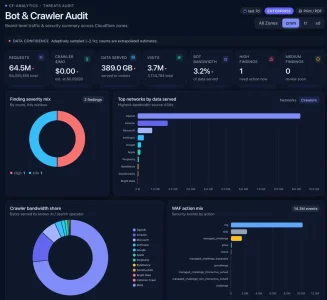
Getting tired of having to analyse Cloudflare HTTP/WAF analytics. So developing newer tools to allow AI to do the heavy lifting for myself and my clients :D Had older tools before, but thought I'd get AI to create from scratch to see what it can do now :)

AI FTW and will roll out to my clients on Cloudflare :cool:

Tool supports profiles for Cloudflare sites. Below is 3 profiles, cmm, tr, sd analysis check test

1782674884365.webp
 
So it's not really a solution on ALL automated detected activity, it's only for those who can afford it. So much for unity of internet; two classes for the win, those who have the money get protection or preferred treatment, the others can go f themselves. Sorry but this is Animal Farm's "all animals are equal with the others, but some are more equal than others"...

Cloudflare enterprise starts at $2k/month, well above what 99% of non-commercial websites can afford. That's a big problem.

You know what really sucks? when you give an AI company money, you help fund this activity that's actively destroying the internet.
The more they scrape, the better their models get, which increases their income, at your expense.
It's adding insult to injury to have to pay them twice.

I decided to invest in local AI to boycott these companies. The cost of entry for an AI server that can serve 8 was $11.5k. But it worked out well.

The cost of building what's effectively a self hosted cloudflare with protection range closer to an enterprise plan than a pro one is under $10k, which is less than a year of hassle / bandwidth charges across my fleet.

The only hope we have:
As the economy of scale looks better and better for defending against this crap, so will the number of available solutions.
But we could end up with a 'papers please' style internet experience if the AI companies want to continue to escalate, and government fails to intervene.
 
.stile = maybe cloudflare turnstile?

didn't make any changes to my CF but only noticed this redirect started happening since last night.

either CF fixed their stuff or XF Cloud added something, either way, thank you.

if you follow the link shows brief message and usually CF has their branding everywhere

1782759753362.webp
 
Last edited:
I can vouch for Cloudflare Enterprise Bot Management it eats bots and crawlers for breakfast :D

Getting tired of having to analyse Cloudflare HTTP/WAF analytics. So developing newer tools to allow AI to do the heavy lifting for myself and my clients :D Had older tools before, but thought I'd get AI to create from scratch to see what it can do now :)

AI FTW and will roll out to my clients on Cloudflare :cool:

Tool supports profiles for Cloudflare sites. Below is 3 profiles, cmm, tr, sd analysis check test
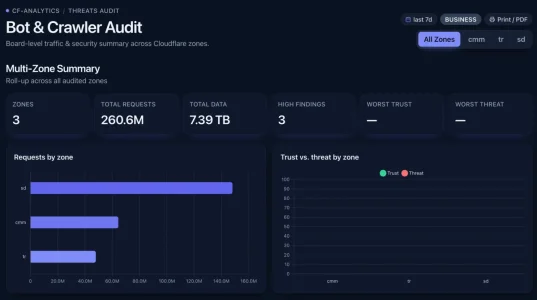
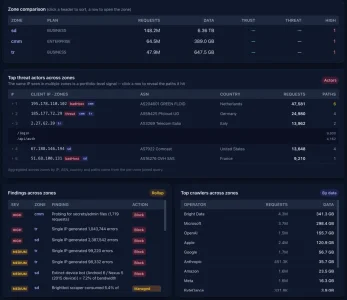
Working on new tools for my clients and my sites on Cloudflare to utilize tools and AI to get indepth insights for Cloudflare HTTP/WAF analytics for individual Cloudflare zone sites but also can aggegrate analytics across zones to come up with patterns and insights that can be actionable. Benefits: Since I have a Cloudflare Enterprise plan site in the mix, means I get more detailed analytics that can be helpful for non-enterprise sites as well :D The more sites to aggregate profiling, the more common bad actor/bots to surface :cool:

Analytics for 3 Cloudflare profiled sites, cmm, tr, sd on CF Enterprise and Business plans with All Zones, cmm, tr, sd tabbed HTML dashboards :)

Preview for some of the dashboards also auto generate new suggested Cloudflare WAF expression rules to try which can be scheduled for weekly and daily runs :D

This is just for 3 sites, haven't tried with up to 200+ sites 🤔

1782760091406.webp
1782760098490.webp
1782760105025.webp
 
I already use cloudflare turnstile. It's ok but it doesn't completely stop the guests.
What does though is places like trend micro which is similar to cloudflare's under attack solution.
So instead of 10 pages worth of guests who are bots, we're down to the usual 2 pages.
 
didn't make any changes to my CF but only noticed this redirect started happening since last night.

either CF fixed their stuff or XF Cloud added something, either way, thank you.

if you follow the link shows brief message and usually CF has their branding everywhere

View attachment 340743

If you are talking about vape.to, its Cloudflare Turnstile enabled across the site
 
We've been running fine since I last posted to this thread but yesterday got hit with a massive attack that resulted in an error 522, and max'd out our resources.
 
I'm seeing the same as usual. That said, every website has it's varying attackers.
What I've seen over the last two days is a small bunch of new ASNs along with some that have been seen in the past but only rarely lately. However, the overall volume is consistent. So it seems the scrapers try some variations regarding sources, possibly as they realize, that the "traditional" source ASNs they use are burned and blocked more and more. It is however not a massive switch until now, rather a bit of experimenting as it seems.
 
What I've seen over the last two days is a small bunch of new ASNs along with some that have been seen in the past but only rarely lately. However, the overall volume is consistent. So it seems the scrapers try some variations regarding sources, possibly as they realize, that the "traditional" source ASNs they use are burned and blocked more and more. It is however not a massive switch until now, rather a bit of experimenting as it seems.

Proxy providers rotate the IPs out and bring in new ones constantly. So it may be a bit of that going on.
 
Back
Top Bottom