
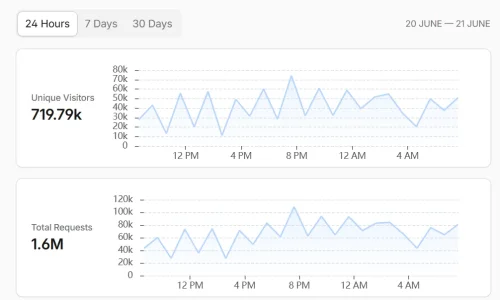
In just over a month with no protections in place, my main site has gone from 100k daily locked down, to now 700k. Slowly getting there to see just how bad this can get.


Interesting reading from the other side of the fence (scrapers), hinting at what other battlegrounds are active these days:
One of the possible filters is the fingerprint of the TLS capabilities announced by the client, which might contradict the source (datacenter/residential) and/or user-agent. Not failproof, but can add one more defensive layer in front of the honey pot (at least temporarily before they tune it well).

I find it ironic how some countries fight against VPNs hosted in local data centers (under the guise of websites) by checking the TLS fingerprint too. As a result, in countries with DPI filtering, perfectly legal websites don't work even within the country. AI content scrapers, government regulators… everyone is fighting against private websitesOne of the possible filters is the fingerprint of the TLS capabilities announced by the client, which might contradict the source (datacenter/residential) and/or user-agent. Not failproof, but can add one more defensive layer in front of the honey pot (at least temporarily before they tune it well).


It's because many of the vpn users use the same ones as the scrapersI find it ironic how some countries fight against VPNs hosted in local data centers (under the guise of websites) by checking the TLS fingerprint too. As a result, in countries with DPI filtering, perfectly legal websites don't work even within the country. AI content scrapers, government regulators… everyone is fighting against private websites
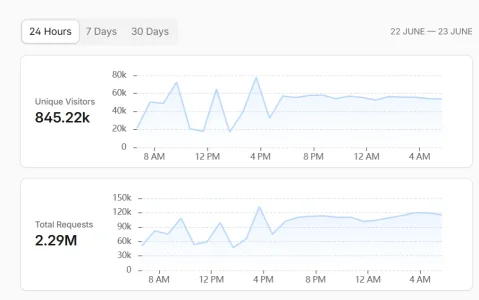
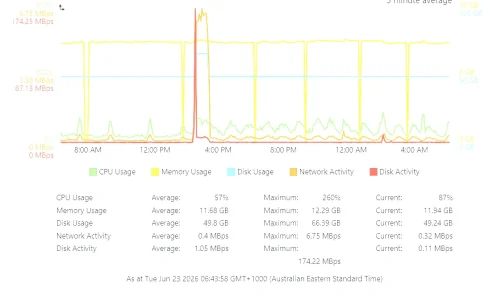
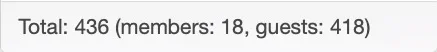
after more than a week of continuous CF "under attack" mode the number of guests on here is way lower than it used to be for ages, but probably still not all are genuine/humans:That's pretty crazy - from 200.000 to 61, finally.
day before yesterday at 5 p.m.
View attachment 340016
at 5:27 (around this time CF "under attack mode" seems to have been set)
View attachment 340017
and at 5:31:
View attachment 340018
yesterday at noon:
View attachment 340015
8 o clock this morning
View attachment 340014
9 o clock this morning
View attachment 340013
just now:
View attachment 340012
I'm sure they're competent enough to tune their server or add some resources if needed to handle it all.It seems a bit embarrassing that XF have nothing to offer in that regard and (avoiding 3rd party add ons on their own forums) have no option for their own forum but to use UAM permanently, as it seems.
Sure, but that's not the point. For one, what is true for the XF crew might not be true for XF customers and secondly: If you ask forum admins what their biggest topic and issues are the answer today would probably be:I'm sure they're competent enough to tune their server or add some resources if needed to handle it all.

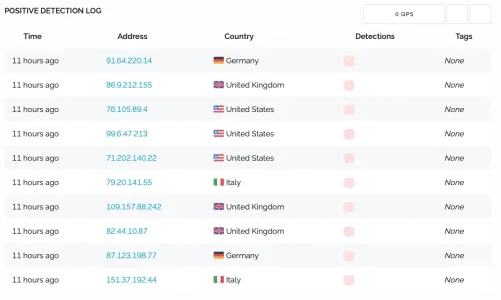
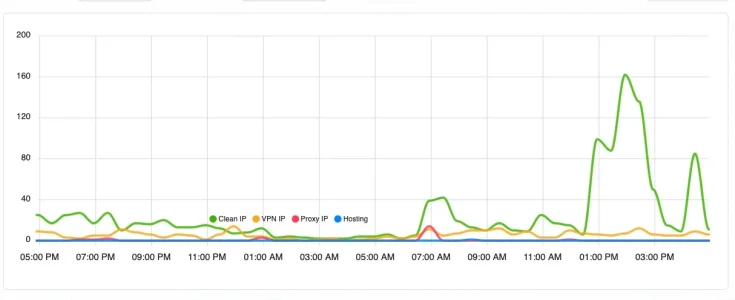
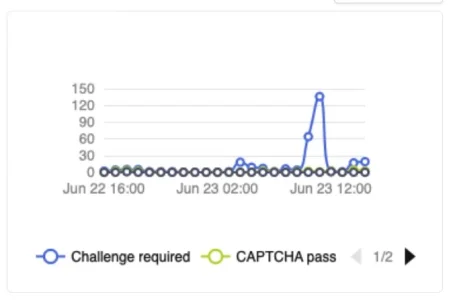
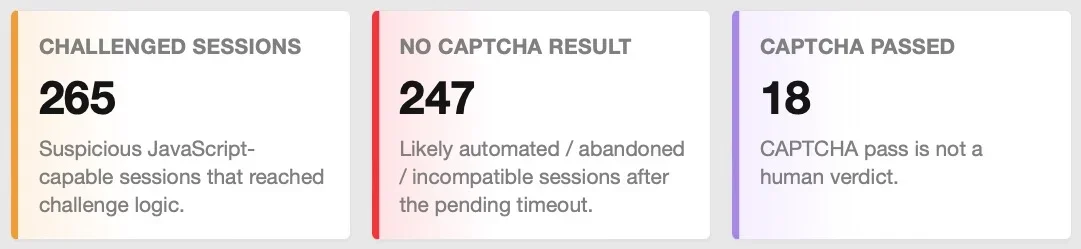
Are you using Bot Guard and another plugin that uses proxycheck?
SEO died 20 odd years ago, the moment Google released localisation and adwords. You could no longer optimise your website for ranking outside what Google deemed your website zone, and then, even within the zone which you have no idea how far it spans, basic SEO still has no real metric difference. You can make two websites today, creates links to one, optimise every aspect of it as you believe works, then build another and do nothing, just make the website the best reflection of the business for the customer, and its not uncommon that the untouched one outperforms the optimised one.we're witnessing the death of SEO
SEO died 20 odd years ago, the moment Google released localisation and adwords. You could no longer optimise your website for ranking outside what Google deemed your website zone, and then, even within the zone which you have no idea how far it spans, basic SEO still has no real metric difference. You can make two websites today, creates links to one, optimise every aspect of it as you believe works, then build another and do nothing, just make the website the best reflection of the business for the customer, and its not uncommon that the untouched one outperforms the optimised one.
Regardless what people think today, with the discussion in this very thread, people blocking everything AI, the difference in my sites daily posting is showing you should not be blocking them, hence I went the highly optimised server route. When I blocked and strangled the AI internet, my daily posting fell slowly from around 125 posts to 50 relying on search engines only, and when unleashed like it is right now, daily posts are about 150+ and climbing steadily.
I use AI a lot for search. If you aren't being found in AI for search because they can't access your site, then you're likely missing out on a lot of potential new traffic and members.
Just my experience playing around with all this, and I used to be one of the top SEO's 20+ years ago, basically I was one of the people you could blame when everything returned porn or similar as a listing. Retired after Google took over and stopped all the nonsense.
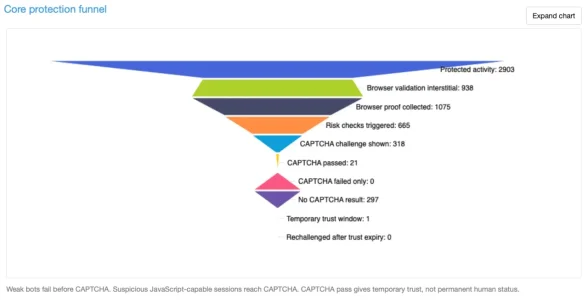
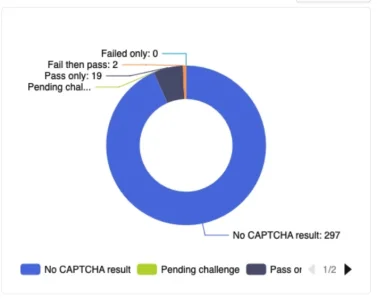
In principe: Yes. But it depends. Through the multi-stage approach it is somewhat difficult to get proper data, the more as IP Threat Monitor currently only has very limited possibilities when it comes to analysis and the .htaccess outcome is a bit of a pain to analyze. Bot Guard does in my configuration only count what has been challenged and what was analyzed but not systematically a simple pass / checked / failed number. I could have it but then the db size would further increase and bot Guard is already somewhat db heavy in terms of size. Also, Bot Guard refers to sessions whereas Threat Monitor acts based on IPs, so not trivial to aggregate that.@smallwheels
Thanks for the info, this sounds like 75% of what i'm designing.
Imagine you're getting pretty effective protection from these layers, no?


We use essential cookies to make this site work, and optional cookies to enhance your experience.

