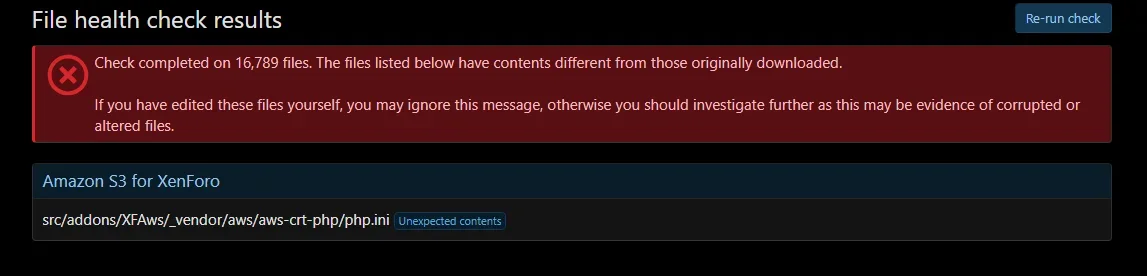
XF 2.3 Compromised file?

This file is included as part of an AWS library bundled with XenForo. It's intended for development purposes and isn't used by XenForo itself.

The file health check indicates that its contents differ from those in the original distribution, but this alone doesn't suggest that your installation has been compromised.

To resolve the warning, you can download a fresh copy of XenForo from the customer area and upload the file from that package, overwriting the existing copy.
 
Assuming the previous file health check passed, the file would have been modified sometime between that check and this one. Unfortunately, it's not possible for me to say what modified it or why.

You might compare it against the file from a fresh download to see if the differences offer any clues.

If I were to speculate, it's possible your hosting provider modified php.ini files indiscriminately in an attempt to mitigate the vulnerability. However, that's just one possibility.
 
I will look into with my host but it says edited today and the contents are:

Code:
extension=modules/awscrt.so

[Session]
session.upload_progress.enabled = Off
 
Back
Top Bottom