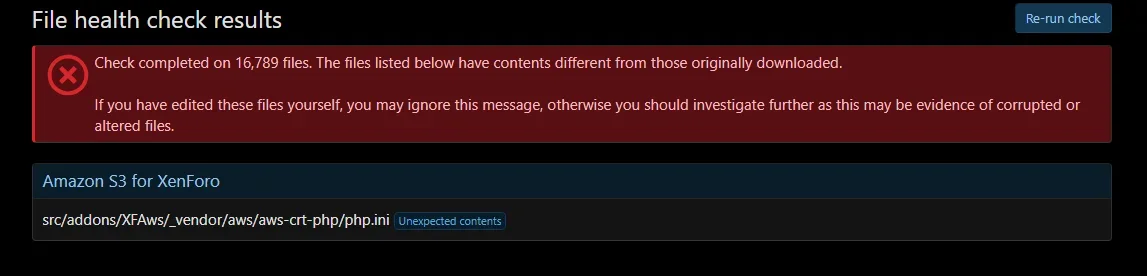
Assuming the previous file health check passed, the file would have been modified sometime between that check and this one. Unfortunately, it's not possible for me to say what modified it or why.
You might compare it against the file from a fresh download to see if the differences offer any clues.
If I were to speculate, it's possible your hosting provider modified php.ini files indiscriminately in an attempt to mitigate the vulnerability. However, that's just one possibility.