
You are using an out of date browser. It may not display this or other websites correctly.
You should upgrade or use an alternative browser.
You should upgrade or use an alternative browser.

[TylerAustin] Google One Tap Sign-In - XF2 1.1.3
No permission to buy ($45.00)
- Author GameNet
- Creation date
Fixes:
- Fixed post-login, post-registration, and account-linking redirects so valid local destinations are preserved while unsafe or external destinations are rejected.
- Fixed protocol-relative, backslash-based, cross-origin, control-character, and excessively long return URL handling.
- Fixed two-step verification handling so a Google account is not connected until the same member successfully completes XenForo's verification flow.
- Fixed registration paths so disabled registration, discouraged-user restrictions, required fields, terms acceptance, age rules, CAPTCHA policy, and pre-registration actions remain enforced.
- Fixed pending email-confirmation redirects and the policy controlling whether an unconfirmed account may be signed in.
- Fixed banned-email checks across sign-in, verified-email matching, registration, and account linking, including fail-closed handling when the policy check cannot be completed.
- Fixed verified-email matching by normalizing surrounding whitespace and requiring Google to report the email as verified.
- Fixed connected-account conflicts so one Google identity cannot be linked to multiple XenForo accounts.
- Fixed a stale legacy-mapping race that could remove a mapping after it had been reassigned.
- Fixed Google key retrieval so failed refreshes do not silently fall back to stale signing keys.
- Fixed setup, listener, cron, controller, and connected-account contracts for XenForo 2.3.
- Fixed automatic log cleanup so each cron run performs a finite, bounded deletion batch.
New Features:
- Added an AdminCP test mode that limits Google One Tap to explicitly permitted XenForo user IDs.
- Added strict test-user validation with positive numeric IDs, duplicate removal, a 100-account limit, and checks for missing accounts.
- Added AdminCP preflight reporting for empty test mode, valid test-account counts, missing user IDs, credentials, callback mode, HTTPS, and origin consistency.
- Added an expiring, single-use continuation for Google account association after XenForo two-step verification.
- Added native Google identity provider data handling for verified One Tap tokens.
Feature Improvements:
- Google sign-in and account association now use XenForo's native connected-account repository as the authoritative identity source.
- Legacy Google mapping records are retained only for compatibility and are no longer trusted as login authority.
- Google key data now uses XenForo's configured cache with native expiry and safely fetches fresh data when no configured cache is available.
- Test mode and test-account settings are now visible in the Testing & maintenance AdminCP options tab.
- Registration now preserves XenForo's pre-registration action key through both automatic and completed-registration flows.
- Connected-account cache rebuilding now follows the native XenForo association flow.
- Admin diagnostic and testing controllers now consistently enforce their dedicated permissions.
Changes:
- Updated the bundled
firebase/php-jwtdependency to the supported 7.x release line.- Set the package requirements to PHP 8.3.0 or newer and MySQL 8.0 or newer.
- Standardized dependency autoloading through the add-on-local Composer bundle.
- Replaced unsupported feature-state caching and runtime method probing with XenForo-native services, repositories, entities, and configured cache access.
- Reworked installation and upgrade handling into deterministic XenForo-native setup steps.
- Removed the obsolete standalone error handler and direct connected-account entity creation.
Notes:
- When test mode is enabled without valid test user IDs, all Google One Tap sign-ins are intentionally rejected.
- Site owners switching between legacy and route-based callback modes must update the authorized redirect URI in Google Cloud.
- Existing connected accounts remain the authoritative source for Google identity ownership.
Documentation Changes:
- Added a customer README covering features, requirements, installation, Google configuration, test mode, privacy, support, and distribution terms.
- Added callback and rollout guidance for site owners configuring Google One Tap.
Support and Security Documentation:
- Documented the Google account information used for sign-in and connected-account association.
- Documented the test-mode safety behavior, two-step verification continuation, safe redirect handling, and log-retention controls.
- Added the current help and support destinations for site owners.
Thank you for your unwavering support and assistance in further enhancing this add-on. This version of the XF2 Add-on includes several bug fixes.
Full Summary
Change:
Bug Fixes:
- Convert the widget into this into one ACP-home info block
- Debug tab is hidden until that option is enabled or XenForo config.php debug mode is on.
- now reads the raw custom_fields JSON, normalizes only the explicit checkbox choice 1, and exposes a strict profile opt-out helper.
- now keeps group-level suppression and per-profile opt-out as separate checks, with strict checkbox-value reading.
- now strips disable_google_one_tap_po from the One Tap completion custom-field payload, excludes it from required-field loading, and saves completion fields through XenForo’s custom-field set when available.
- Removed googleOneTap_test_callback from options.xml
- Removed the now-unused raw option callback renderer Option/TestConnectedAccountButton.php.
- Deleted the now-dead inline renderer TestButton.php
- Allowed-page option validation now rejects URL/protocol-relative input even when negated, so it stays path-pattern only
- Same-site return URL checks now reject absolute URLs with embedded user/pass info in both One Tap and connected-account callback flows
- Connected-account avatar/profile URL rendering now uses explicit attribute escaping
- Google connected-account renderer now rejects URL values with control/space characters before they reach templates
- Mirrored avatar URL hardening in the One Tap and connected-account controllers.
- Rework the setup.php and Listener.php files
- Removed setup repair/default seeding logic from Setup.php (line 20); it now only manages the add-on tables and opt-out user field.
- Removed the bad add-on self-map from _files/autoload.json (line 1) and kept only the Firebase JWT vendor map.
- Fixed the public and admin browser tab title to force Connected accounts, not just accounts
- Hardened the connected-account OAuth return URL so it only redirects to local/same-site URLs
- Escaped the connected-profile fetch URL and the Google Maps option values
Thank you for your unwavering support and assistance in further enhancing this add-on. This version of the XF2 Add-on includes several bug fixes.
Full Summary
Bug Fixes:
- now reads the raw custom_fields JSON, normalizes only the explicit checkbox choice 1, and exposes a strict profile opt-out helper.
- now keeps group-level suppression and per-profile opt-out as separate checks, with strict checkbox-value reading.
- now strips disable_google_one_tap_po from the One Tap completion custom-field payload, excludes it from required-field loading, and saves completion fields through XenForo’s custom-field set when available.
Thank you for your consistent support and assistance in improving this add-on. This version of the XF2 Add-on includes several bug fixes and enhancements.
Full Changelog:
Change:
Bug Fixes:
- Updated firebase/php-jwt from v7.0.3 to v7.0.5.
- Removed the login-page and register-page template modification from template_modifications.xml
- The login form and register form no longer gets a .google-one-tap-container injected above it.
- On /login, the script now removes any old injected container and skips google.accounts.id.renderButton(...).
- The One Tap popup still runs through google.accounts.id.prompt().
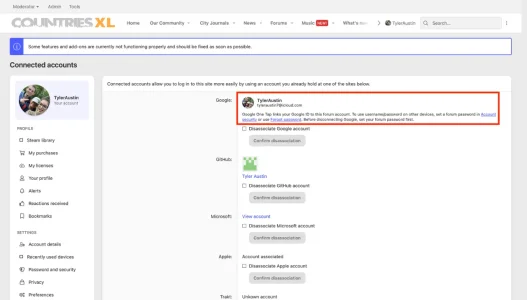
- Keeps the associated Google-account card rendering reliably instead of collapsing to empty/generic output.
- Added DB fallback when provider_data entity access fails under third-party XF extensions.
- Callback handling now consistently respects the global enable flag and googleOneTap.use policy, and reads JSON/raw request bodies properly.
- Restored fixed missing XF\Entity\UserProfile extension registration is in place, so the user opt-out normalization code is actually active after rebuild/import.
- Fixed the connected-account profile JS so root-relative local avatar URLs render, not just absolute http(s) URLs.
- Fixed profile/avatar URLs is not rendering in connected account page
Attachments
Thank you for your consistent support and assistance in improving this add-on. This version of the XF2 Add-on includes several bug fixes and a few changes.
Full Changelog:
- Added mask + reveal behavior on Google connected-account provider ACP page (client ID + client secret fields):
- Switched these options to callback renderers so they are password-masked by default:
- Hardened setup constants and reuse (ADDON_ID) to reduce drift.
- Added legacy option-group migration cleanup (google_one_tap -> googleOneTap) and uninstall cleanup for both IDs.
- Fixed log table backfill safety: when log_id is added in fallback mode, it now gets setDefault(0) to avoid strict-schema insert failures.
- Added defensive table/column existence checks before provider-link migration to avoid SQL failures on partial/odd installs.
- Added safe tableExists() helper and used it in provider migration flow.
- Hardened group detection in templaterMacroPreRender() with OptionGroup type checks (prevents invalid access warnings).
- Hardened callback CSRF behavior: If Google g_csrf_token is absent, controller now requires valid XenForo CSRF token.
- Replaced fragile phrase-key usage in tab labels with stable literals (no phrase dependency regressions).
- Removed suppressed logging and made debug logging safer (isDebugEnabled() + user id only).
- Added strict_types and made handler final.
- Fixed method signatures to be compatibility-safe across XF handler variations (...$extra variadics).
- Added recursion guard to prevent self-trigger logging loops.
- Removed internal XF::logError() recursion risk; now writes to PHP error log directly.
- Added request-context safety for non-web/edge contexts.
- Added URI/token redaction and truncation to reduce sensitive data leakage and oversized log entries.
- Hardened serialized-data handling to prevent object deserialization via allowed_classes => false.
- Fixed table-name resolution fallback in user entity logic so installs with atypical DB prefix/table setups don’t fail lookup/upsert paths.
- Fixed optional client-id validator mismatch so empty client ID is accepted where intended.
- Fixed provider-data class inheritance bug (namespace/import correctness):
- Fixed DB schema detection bug for provider_data column type (safer SHOW COLUMNS handling):
- Fixed potential runtime break when third-party add-ons change XF:Login->completeLogin() signature.
- Added a compatibility wrapper and switched to redirect after login completion.
- Added missing One Tap opt-out enforcement in legacy login controller:
- Added missing One Tap opt-out + banned-email enforcement in legacy user login controller:
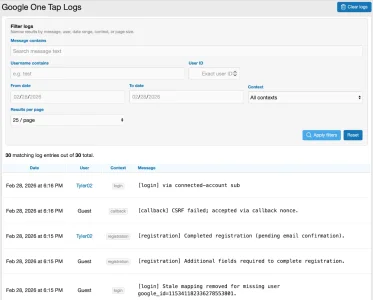
- Added powerful filters in AdminCP Log Viewer:
- message search
- username contains
- user ID
- date range (from / to)
- context filter (auto-detected from log tags like [callback], [login], [connected])
- per-page size (25/50/100/200)
- Added context column for each log row.
- Added truncation + expand (<details>) for very long log messages.
- Added filtered-clear behavior:
- if filters are active, “Clear filtered logs” only deletes matching rows
- if no filters, clears all logs as before
- Added matching/total counter at top of the page.
- Upgraded vulnerable JWT dependency to remove the current advisory:
- Vendor updated to firebase/php-jwt v7.0.3.
- Added a new ACP option googleOneTap_enable_failures_widget (default 0 / OFF) to control failures-widget visibility for both front-end and AdminCP widget contexts.
Attachments
Thank you for your unwavering support and assistance in further enhancing this add-on. This version of the XF2 Add-on includes several bug fixes and changes.
Full Changelog(s):
- Schema-safe connected-account upsert now fills required custom columns (including extra_data) when they have no default:
- Added generated-column guard so DB-generated fields are not inserted:
- Increased One Tap callback fetch abort timeout from 15000 to 45000 to reduce false client aborts on slower callback processing:
- Added missing repository init in completion action:
- Fixed callback logic so mapped users who are blocked (including email_confirm when option is OFF) are not treated as stale and deleted:
- Added explicit blocked-login message for email_confirm when option is OFF: