You are using an out of date browser. It may not display this or other websites correctly.
You should upgrade or use an alternative browser.
You should upgrade or use an alternative browser.
Heads up - critical PHP patch needed tomorrow for all servers
- Thread starter ES Dev Team
- Start date


On server update at 9.15am
"The security fixes have been backported into the existing PHP releases, so the version number shown in cPanel, phpinfo() or WordPress Site Health won't change.
** Patched servers will still report the same PHP version (5.2–8.5) as before, but are running the fixed build. **
** There's no need to change your PHP version or contact us to confirm your site is protected. **""
Sound ok?
Last edited:

On server update at 9.15am
"The security fixes have been backported into the existing PHP releases, so the version number shown in cPanel, phpinfo() or WordPress Site Health won't change.
** Patched servers will still report the same PHP version (5.2–8.5) as before, but are running the fixed build. **
** There's no need to change your PHP version or contact us to confirm your site is protected. **""
Sound ok? I'd be happier if I saw the number change to 8.3.36
They can't just blindly upgrade everyone to that, some people are running specific versions and it could cause more problems.
Backporting is the right move, if everything on your side is up to speed and can jump to 8.3.36, then request it.

Is there a way to know which PHP version a remote website is using ?
Can I figure out what php version Xenforo.com is using ? (as an example).
Can I figure out what php version Xenforo.com is using ? (as an example).

admin.php?tools/phpinfoIs there a way to know which PHP version a remote website is using ?
Can I figure out what php version Xenforo.com is using ? (as an example).

Is there a way to know which PHP version a remote website is using ?
Can I figure out what php version Xenforo.com is using ? (as an example).
Nope usually not. There are options to display it in headers etc. but it’s usually wise to remove those to make it harder for people to find servers running vulnerable versions.
But if you’re interested, we’re running PHP 8.3.36.
I haven't had much luck with the php2shell checkers, like this one:
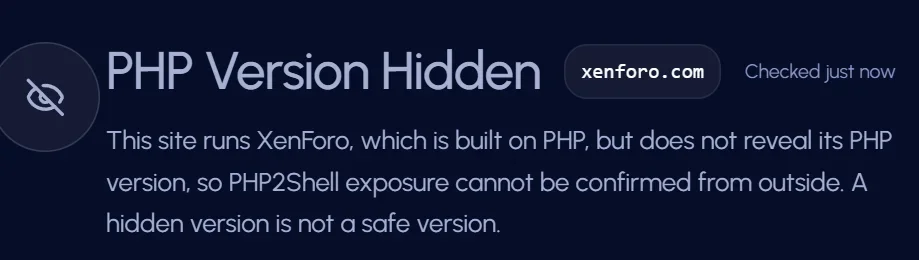
https://atlas.brandefense.io/php-vulnerability-check


I can see that could be an issue though - but yes I can upgrade.They can't just blindly upgrade everyone to that, some people are running specific versions and it could cause more problems.
Backporting is the right move, if everything on your side is up to speed and can jump to 8.3.36, then request it.
Also if they've patched it why are they still saying this?
"Please don't switch session.upload_progress.enabled back on. We've turned it off for you as part of the fix."
Last edited:
Good. It’s sensible not to advertise your specific PHP version.

Any guidance on CVE-2026-115560?
From an article:
If we're only running XenForo, should there be an issue?
From an article:
Only a narrow setup is at risk. PHP says the problem can occur when a web application does all of the following: sets the session.serialize_handler option to php_binary or php_serialize in its configuration, then changes that option to php while running by calling ini_set(), and makes that change before it calls session_start().
If we're only running XenForo, should there be an issue?
"The project is not issuing an emergency fix for it. Instead, it recommends turning off a feature called session upload progress until a fix is available in the next routine release."Any guidance on CVE-2026-115560?
From an article:
If we're only running XenForo, should there be an issue?
My server already said yesterday that session upload progress was turned off as part of the fix so maybe servers already know about this other one?

Any guidance on CVE-2026-115560?
From an article:
If we're only running XenForo, should there be an issue?
Yes. The PHP team suggests remediating for now.
This remediation should cover new / old versions of php and also all 3 CVEs:
Code:
#Courtesy mitigations, updated 10/23/2026
#rationale: https://github.com/syhunt/php2shell-protection
session.upload_progress.enabled = Off
memory_limit = -1
post_max_size = 32M
upload_max_filesize = 28M

#possibly break some applications
session.use_strict_mode = 1
session.cookie_httponly = 1
session.cookie_secure = 1
Working and tested on 10 different kinds of apps including two xenforo forums.
max upload size, you will need to warn your members about. The best advice to them is to upload 1-2 images at a time. Otherwise a big batch will fail.
You may not need all these mitigations so check the github repo as it explains each line.
Of course you should upgrade your PHP also like a good sysadmin.

xenforo itself probably doesn't need or perhaps even rely on session.upload_progress.enabled anyway."The project is not issuing an emergency fix for it. Instead, it recommends turning off a feature called session upload progress until a fix is available in the next routine release."
My server already said yesterday that session upload progress was turned off as part of the fix so maybe servers already know about this other one?
@Chris D
Only a narrow setup is at risk. PHP says the problem can occur when a web application does all of the following: sets the session.serialize_handler option to php_binary or php_serialize in its configuration, then changes that option to php while running by calling ini_set(), and makes that change before it calls session_start().