It was back porting as I updated my CMM to 8.5.12 about 1 hour ago.Some people have PHP7.4, which is waiting for @eva2000 backporting, so I've taken their sites offline.

You are using an out of date browser. It may not display this or other websites correctly.
You should upgrade or use an alternative browser.
You should upgrade or use an alternative browser.
Heads up - critical PHP patch needed tomorrow for all servers
- Thread starter ES Dev Team
- Start date

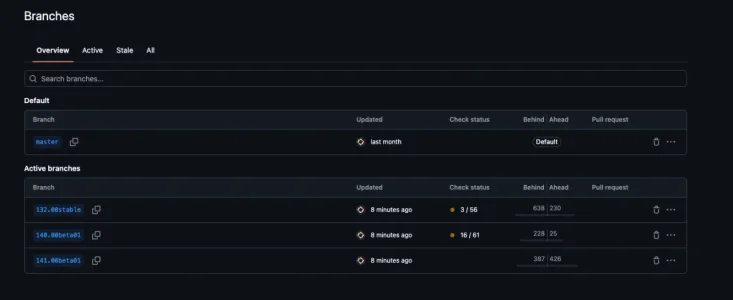
He's still working on it I think, as I keep seeing GIT commitsIt was back porting as I updated my CMM to 8.5.12 about 1 hour ago.
Code:
 21 files changed, 4937 insertions(+), 31 deletions(-)
 create mode 100644 patches/php/php7234-cve-2026-109618.patch
 create mode 100644 patches/php/php7331-cve-2026-109618.patch
 create mode 100644 patches/php/php742-7.4-cve-2026-109618.patch
 create mode 100644 patches/php/php80-8.0-cve-2026-109618.patch
 create mode 100644 patches/php/php81-8.1-cve-2026-109618.patch
Updated to 650c173 backport PHP 8.2.35 security fixes to PHP 7.2-7.3 EOL in 132.00stable.
Latest commit: 650c173 (2026-10-22)
backport PHP 8.2.35 security fixes to PHP 7.2-7.3 EOL in 132.00stableThis was an hour ago.He's still working on it I think, as I keep seeing GIT commits
[09:52][root@site.com centminmod]# cmupdate
-------------------------------------
Updating Centmin Mod code
-------------------------------------
* 140.00beta01
Checking for updates on origin/140.00beta01 ...
remote: Enumerating objects: 26, done.
remote: Counting objects: 100% (26/26), done.
remote: Compressing objects: 100% (2/2), done.
remote: Total 15 (delta 13), reused 15 (delta 13), pack-reused 0 (from 0)
Unpacking objects: 100% (15/15), 14.96 KiB | 1.25 MiB/s, done.
From https://github.com/centminmod/centminmod
* branch 140.00beta01 -> FETCH_HEAD
b289668..691534f 140.00beta01 -> origin/140.00beta01
Fast-forwarding 140.00beta01 to origin/140.00beta01 ...
Updating b289668..691534f
Fast-forward
centmin-cli.sh | 2 +-
centmin.sh | 2 +-
inc/php_patch.inc | 12 +-
installer82.sh | 6 +-
installer83.sh | 6 +-
installer84.sh | 6 +-
installer85.sh | 6 +-
patches/php/php742-7.4-cve-2026-109618.patch | 937 +++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
patches/php/php80-8.0-cve-2026-109618.patch | 945 ++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
patches/php/php81-8.1-cve-2026-109618.patch | 1180 +++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
10 files changed, 3085 insertions(+), 17 deletions(-)
create mode 100644 patches/php/php742-7.4-cve-2026-109618.patch
create mode 100644 patches/php/php80-8.0-cve-2026-109618.patch
create mode 100644 patches/php/php81-8.1-cve-2026-109618.patch
Updated to 691534f backport PHP 8.2.35 security fixes to PHP 7.4-8.1 EOL in 140.00beta01.
Already up to date.
Latest commit: 691534f (2026-10-22)
backport PHP 8.2.35 security fixes to PHP 7.4-8.1 EOL in 140.00beta01
-------------------------------------
Updated Centmin Mod code
-------------------------------------
My server still hasn't updated my php from 8.3.35 - it says they have mitigations in place disabling php's upload progress tracking. They have an updates page but it hasn't updated since 7.30pm It's making me slightly nervous, so I've taken the site offline at the Cloudflare side by just blocking the site with a notice page. Is that enough?

I'm just finishing updating my fleet and i'm glad i did the mitigations last night;
Unfortuantely yes, Xenforo does not take well to them, but it works on other apps.
PHP team offered some other good mitigations if you're unable to upgrade.
Unfortuantely yes, Xenforo does not take well to them, but it works on other apps.
PHP team offered some other good mitigations if you're unable to upgrade.

Mine's the same but i'm not going that far.My server still hasn't updated my php from 8.3.35 - it says they have mitigations in place disabling php's upload progress tracking. They have an updates page but it hasn't updated since 7.30pm It's making me slightly nervous, so I've taken the site offline at the Cloudflare side by just blocking the site with a notice page. Is that enough?
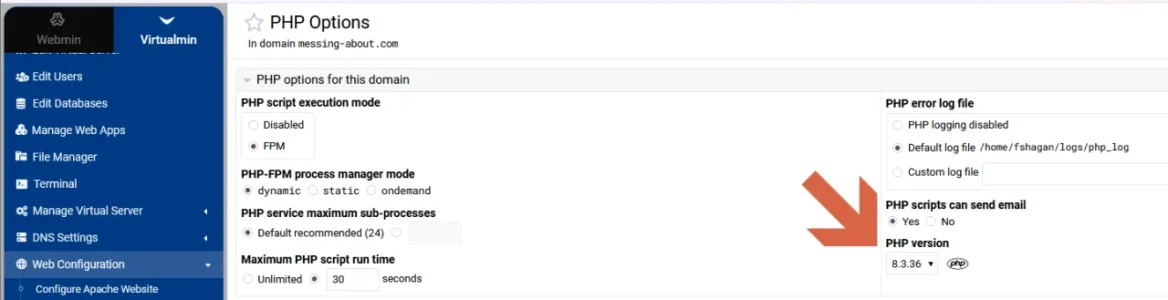
Just updated my forums to 8.3.35 (latest 8.3 version the remi respository was showing) pending updating to 8.3.36 (the patched version). After updating my VPS, I checked and it looks like the remi repository has the update to 8.3.36 and it installed it:
I'm using Webmin/Virtualmin for my VPS.
Code:
  php83-php-cli-8.3.36-1.el8.remi.x86_64
  php83-php-common-8.3.36-1.el8.remi.x86_64
  php83-php-fpm-8.3.36-1.el8.remi.x86_64
  php83-php-gd-8.3.36-1.el8.remi.x86_64
  php83-php-gmp-8.3.36-1.el8.remi.x86_64
  php83-php-intl-8.3.36-1.el8.remi.x86_64
  php83-php-mbstring-8.3.36-1.el8.remi.x86_64
  php83-php-mysqlnd-8.3.36-1.el8.remi.x86_64
  php83-php-pdo-8.3.36-1.el8.remi.x86_64
  php83-php-pspell-8.3.36-1.el8.remi.x86_64
  php83-php-xml-8.3.36-1.el8.remi.x86_64
I'm using Webmin/Virtualmin for my VPS.

Ta Da https://community.centminmod.com/th...-updates-and-eol-php-7-4-8-1-backports.33134/ !By patching everything as soon as possible. Some tweaking of my own stuff to use Remi repos rather than OS versions as well.
WAF from Cloudflare, cPFence, Imunify360 and still pending Cloudlinux to release the alt-php versions which they are building.
Some people have PHP7.4, which is waiting for @eva2000 backporting, so I've taken their sites offline.
Never-ending commit stream

It's tested and settled now for Centmin Mod users and there's a test script to confirm if Centmin Mod PHP-FPM version has fixed the security issues too https://community.centminmod.com/th...-updates-and-eol-php-7-4-8-1-backports.33134/

We run a XenForo 2.2.12 forum on PHP 7.4.33, with numerous add-ons and customizations, behind Cloudflare.Correct it is now on Remi's repo. How you get it installed matters little. If you're running PHP 8.3 then you need PHP 8.3.36.
Following the PHP2Shell vulnerabilities, our developer recommends switching immediately to PHP 8.2.35, without first checking compatibility with all our add-ons. A test forum works on PHP 8.2, but it does not include our add-ons, so the full setup remains untested.
We had already planned to upgrade to XenForo 2.3, but our schedule is currently tight, and completing that upgrade at short notice would be difficult.
Does the severity of these vulnerabilities justify switching PHP immediately despite the risk of breaking the live forum, or is it reasonable to rely temporarily on Cloudflare’s protections while we complete compatibility testing? What minimum checks would you recommend before proceeding?

I stopped reading here. Yes.Does the severity of these vulnerabilities justify switching PHP immediately
I just mention it here for others since the Announcement indicates it isn't available through Remi's repo. It now is.Correct it is now on Remi's repo. How you get it installed matters little. If you're running PHP 8.3 then you need PHP 8.3.36.

Hmm I stayed on an older php version because my linux distro provided a patch for it. Just had to do apt update / apt upgradeWe run a XenForo 2.2.12 forum on PHP 7.4.33, with numerous add-ons and customizations, behind Cloudflare.
Following the PHP2Shell vulnerabilities, our developer recommends switching immediately to PHP 8.2.35, without first checking compatibility with all our add-ons. A test forum works on PHP 8.2, but it does not include our add-ons, so the full setup remains untested.
We had already planned to upgrade to XenForo 2.3, but our schedule is currently tight, and completing that upgrade at short notice would be difficult.
Does the severity of these vulnerabilities justify switching PHP immediately despite the risk of breaking the live forum, or is it reasonable to rely temporarily on Cloudflare’s protections while we complete compatibility testing? What minimum checks would you recommend before proceeding?
Another heads up.
If you use the ondrej ppa to install and can't pull down patches because you're seeing 503.. the problem is likely you run the old repo for it
here is your solution:
If you use the ondrej ppa to install and can't pull down patches because you're seeing 503.. the problem is likely you run the old repo for it
here is your solution:
Code:
First, google how to remove the launchpad ppa for your particular version of ubuntu,
then copy and paste this to a bash script and execute it as admin:


#!/bin/sh
# To add this repository please do:

if [ "$(whoami)" != "root" ]; then
    SUDO=sudo
fi

${SUDO} apt-get update
${SUDO} apt-get -y install lsb-release ca-certificates curl
${SUDO} curl -sSLo /tmp/debsuryorg-archive-keyring.deb https://packages.sury.org/debsuryorg-archive-keyring.deb
${SUDO} dpkg -i /tmp/debsuryorg-archive-keyring.deb
${SUDO} sh -c 'echo "deb [signed-by=/usr/share/keyrings/debsuryorg-archive-keyring.gpg] https://packages.sury.org/php/ $(lsb_release -sc) main" > /etc/apt/sources.list.d/php.list'
${SUDO} apt-get update