Fixed DKIM verification stuck — domainkey record format changed?

lanbin

Member
Licensed customer
Affected version
2.3.9
Hi,

I'm having issues with DKIM verification.
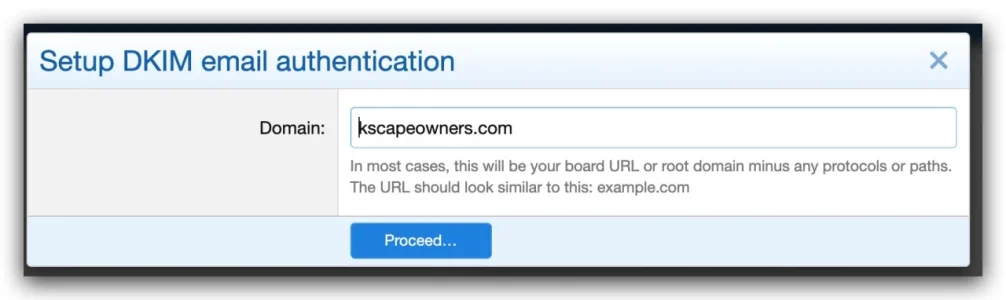
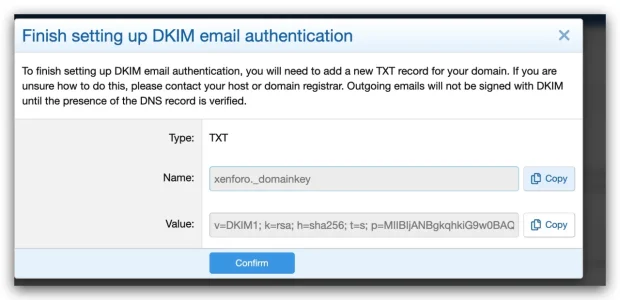
As far as I remember, earlier the record used to look like xenforo._domainkey, but now when generating it just shows ._domainkey.
Previously the verification would pass in about 2 minutes, but now it's been over an hour and I'm still seeing this message:

"Attempting to verify your DNS record but it may take up to 24 hours for DNS changes to propagate. If it has been longer, you may need to verify your entries."
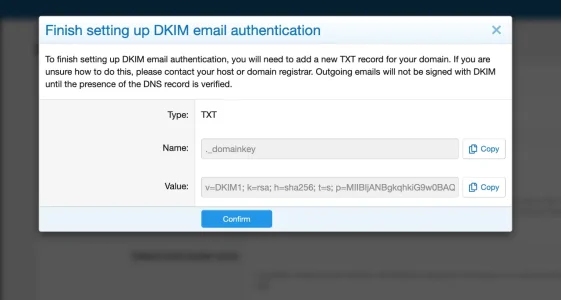
 

Attachments

  • DKIM.webp
    DKIM.webp
    34.6 KB · Views: 38
I've tried to set up DKIM recently as well with no luck. Several tries but no avail. It seems to be trickier than it should be, given that there are a bunch of threads from people having issues with it.

One thread that I found particularly useful is this one:


including this post with a hint that I wasn't able to try until now.

Others around the topic are i.e. these:


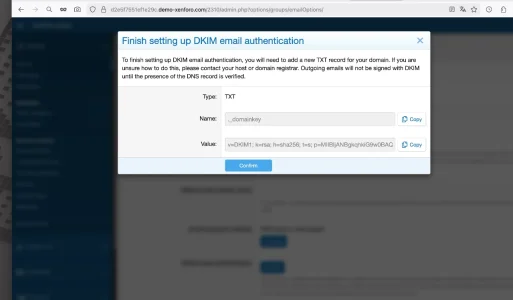
The DKIM issue still remains in XenForo version 2.3.10. Today, out of curiosity, I created a test forum: https://d2e5f7551ef1e29c.demo-xenforo.com/2310/admin.php
(You may log in as the administrator with the username admin and password admin). There, the system similarly generates ._domainkey instead of xenforo._domainkey. After that, I wait 24 hours and still receive the same error.

@Chris D
 

Attachments

  • DKIM.webp
    DKIM.webp
    33 KB · Views: 30
Do you have access to your mail server? DKIM should be configurable there. I do not use the XF setting.
Obviously it heavily depends what way of mailing one is using. If you use an external/seperate mail server for relaying there is no need for DKIM configuration within XF. If you use the built-in mailer you will have the need, if you want to use DKIM.
 
I use an external SMTP server managed by Amazon SES. I reported this to XenForo. They've informed me this morning that it's a known issue, and that it'll be addressed in the next released version after 2.3.10.
 
I use an external SMTP server managed by Amazon SES. I reported this to XenForo. They've informed me this morning that it's a known issue, and that it'll be addressed in the next released version after 2.3.10.
Why would you need to set up DKIM within XenForo if you are using an external smtp-server?
 
Why would you need to set up DKIM within XenForo if you are using an external smtp-server?
It's a fair question. The honest reason is We migrated from a self-hosted server to a XenForo hosted server. We used to use the built-in mailer, and the DKIM were working just fine. We later moved to use Amazon SES and we started receiving complaints that our emails were being sent to folks' SPAM folders. Sometimes DKIM signatures would pass, but sometimes they would fail and I couldn't figure out why.

In case there was some weird errant PHP mailer code still sitting on the server somewhere, I thought I'd cover my bases. Probably a wild goose chase, but I wanted to cover all possibilities.
 
Probably a wild goose chase
Very. If you don't use the built in mailer (which is a binary setting: either you do or you don't) DKIM-sttings within XF are not used either. You possibly have a DKIM-settings-issue with your Amazon-mailer-setup but this has nothing to do with the topic of this thread.
 
If you don't use the built in mailer (which is a binary setting: either you do or you don't) DKIM-sttings within XF are not used either.
This is not correct. XenForo will sign emails if DKIM is successfully enabled no matter which transport (mail(), SMTP, etc.) is used.
 
XenForo will sign emails if DKIM is successfully enabled no matter which transport (mail(), SMTP, etc.) is used.
:oops: Honestly? I am no DKIM expert but had assumed that DKIM would be a thing for a SMTP server and would be not used if XF acts as an SMTP client. Is this normal/expected behavior or rather misbehavior/a bug?
So if one uses XF as an SMPT client one should disable DKIM manually to avoid trouble? Or does it even have advantages when it is still turned on?
 
You assumed wrong :)

It would be technically perfectly fine (though uncommon and probably unwanted / unnecessary in most cases) if both XenForo and the MTA sign an email (using distinct selectors / keys).

Personally i'd always sign at MTA / SMTP server if possible. IMHO much easier/ reliable / performant than via PHP, but not every SMTP provider offers DKIM signing.
 
I've recently been trying to get this to work also. I upgraded to XF2.3.12 and when I try to enable DKIM authentication, it first gave me a 'xenforo._domainkey' key selector, and I think it did verify the DNS record; but it would still not sign the outgoing emails. Then I went to 'change' the DKIM authentication, and now every time I do that, I get a different key selector, usually starting with xf-{string of characters}. Tried waiting for a couple of days to for the DNS record verification to work, but even though easydmarc, mxtoolbox and everyone else was able to see the dkim key/value pair, I had no success from within the xenforo control panel setup.

then I hit 'disable' on the DKIM authentication, saved it, went back and re-enabled and it gave me ".domainkey" as the selector. Is that even valid? How is that supposed to be entered in the DNS record name field?


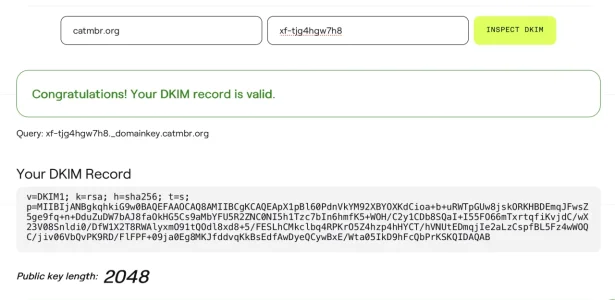
Update: The XF DKIM setup gave me the selector "xf-hax_8as30l". I ran the DKIM test on easydmarc.com, mxtoolbox.com and then https://dmarcian.com/dkim-inspector/. The last one says the following:
"

There is something wrong with your DKIM record.​

DKIM selectors must not contain underscore characters per RFC 6376. Compliant receivers are likely to ignore this invalid DKIM record, or simply declare its usage as 'fail'​

"​

So, this seems to be an issue with the XF selector name generation, at least when it does not give you '._domainkey' as a selector, or 'xenforo._domainkey'. We do not seem to be able to select our own domain selector here, so I can't test different values.
I recall that the previous couple of non-default domain selectors it generated, also had underscores in the text after xf-{string}.
 
Last edited:
@Anthony Parsons Does that work only if XF decides that "._domainkey" is the selector?

This morning I selected 'change' again in the DKIM authentication setup panel. It gave me a selector without underscores, so I updated my DNS accordingly. Two minutes later, I got a 'valid' result from dmarcian.com. Meanwhile, my XF installation is still stuck in the "attempting to verify" state...

So, there must be something else not going right here. I copy-pasted the selector and the record itself directly from the XF setup panel fields.

Screenshot 2026-08-04 at 7.24.24 AM.webp
 
Thank you for reporting this issue, it has now been resolved. We are aiming to include any changes that have been made in a future XF release (2.3.14).

Change log:
Show the newly saved DKIM selector during setup and generate DNS-safe selectors
There may be a delay before changes are rolled out to the XenForo Community.
 
Back
Top Bottom