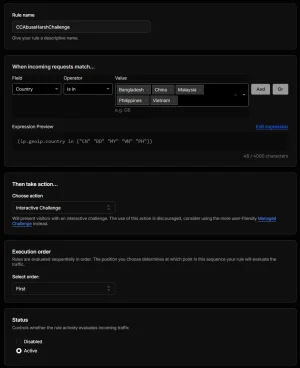
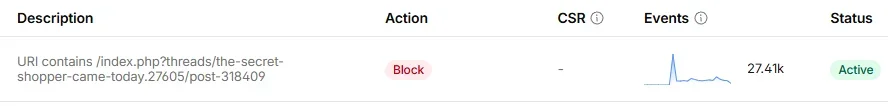
I took a look at a different block.
What length of time frame are we talking about here?
This looks much closer to a Botnet performing a DDOS than it does AI mass-scraping.
Basically often hard to tell the difference - the more as in this case the target was one single URL, which then means either DDOS or a misconfigured scraping attempt. Given that most of the IPs are data center IPs and the ASNs involved are well known for hosting scrapers and resident proxies it can be assumed that, whatever it was, did use the same infrastructure that the scrapers use and that is was a rented professional proxy infrastructure. It does not seem plausible that tens of thousands of IPs in datacenters would be legally rented as own servers (way too much cost and effort) and also not that they would/could all be hacked/taken over as then there would typically be the majority private computers and those within data centers wold have a way different distribution. The ASNs involved are again for the most part well known for being part of the filthy part of the internet - so it is a pretty safe guess that this is a rented professional proxy infrastructure from one or more providers of residential proxies - the same as is used for scraping but also for DDOS attacks.
The Top 20:
ASN 212238: Datacamp Limited, 30192 IPs
ASN 9009: M247 Europe SRL, 21591 IPs
ASN 3257: GTT Communications Inc., 17696 IPs
ASN 22773: Cox Communications Inc., 11000 IPs
ASN 210906: UAB Bite Lietuva, 10774 IPs
ASN 203020: HostRoyale Technologies Pvt Ltd., 9571 IPs
ASN 62874: Web2Objects LLC., 8026 IPs
ASN 7979: Servers.com Inc., 7517 IPs
ASN 46635: Contact Consumers, 7415 IPs
ASN 11798: Ace Data Centers Inc., 7250 IPs
ASN 396356: Latitude.sh, 6601 IPs
ASN 396319: Oxylabs, 5395 IPs
ASN 398781: OCULUS NETWORKS INC, 5015 IPs
ASN 55286: B2 Net Solutions Inc., 3878 IPs
ASN 401152: Ace Data Centers II L.L.C., 3869 IPs
ASN 212286: LonConnect Ltd, 3664 IPs
ASN 134450: HostRoyale Technologies Pvt Ltd, 2959 IPs
ASN 132817: DZCRD Networks Ltd, 2460 IPs
ASN 209709: UAB code200, 1702 IPs
ASN 7015: Comcast Cable Communications LLC, 1303 IPs
They are all present in the other dataset as well and most of them can be considered "bad-to-the-bone" ASNs while some might just be "ignorant". Only one of them is new to me as "not yet part of my blocking list": Never seen
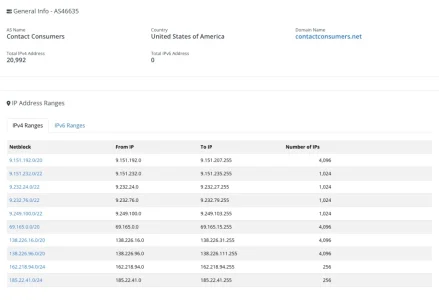
ASN 46635: Contact Consumers. It seems to be relatively small and pretty new as well:
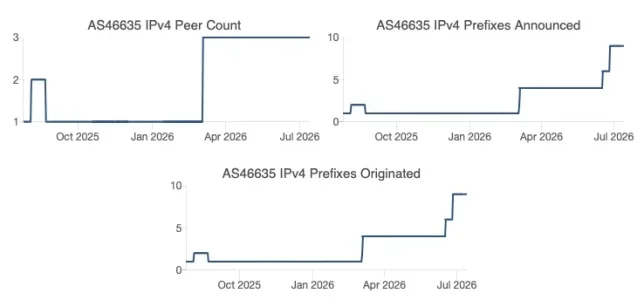
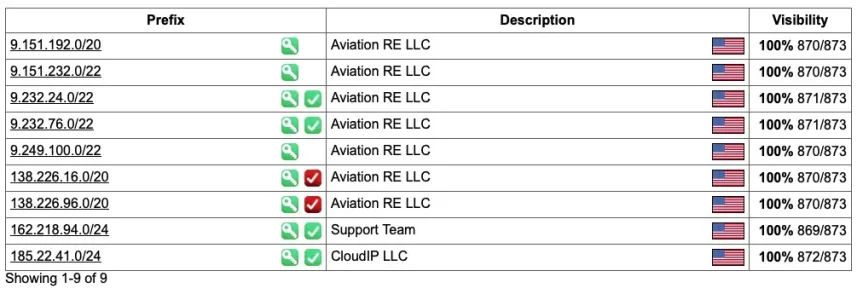
which explains, why it might not have hit me yet.
It is btw. peering with ASN 3257: GTT Communications Inc., which is well known for bad actors, much bigger and, while mainly US based, has some IPs abroad as well:
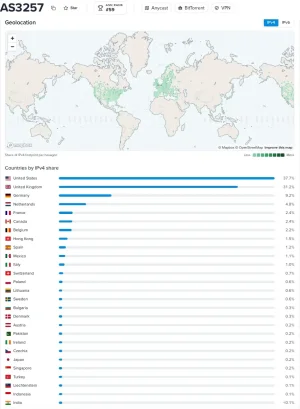
GTT as well as Cox and Comcast are upon other connection types all offering DSL/Cable for private users as well, yet still all three are well known for loads and loads of trash coming from their networks. Apart from these three, all the others can be completely blocked w/o any harm and should be blocked as well.
Also the numbers show that the providers that host these filthy IPs probably do make quite some money with them. Hard to believe, given the amount of IPs involved, that they never received complaints - rather likely that they ignore complaints for their own profit and thus have knowingly become part of the filthy business they support. The consequence is that they should be blocked completely.
How you deal with GTT, Cox and Comcast depends from if you do have users from the US and if so if they use one of those providers for their internet connection (which may be way more probable with Cox and Comcast than with GTT). I've blocked all of their ASNs (as they've all been very notorious in the past) and never looked back. Huge relief, but then I don't have many users from the US.




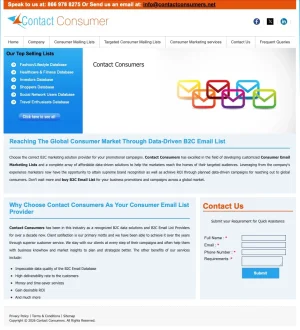
 One could further ask oneself what such a company would do with 21.000 IP-adresses.... Well, possibly one should block them for smtp as well I guess.