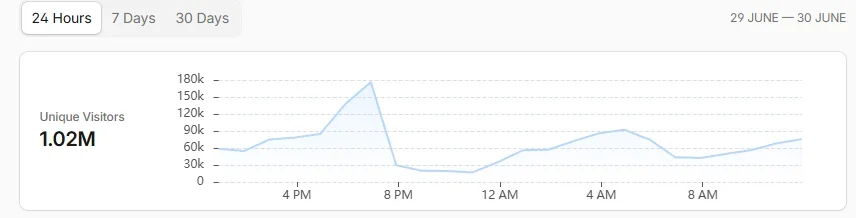
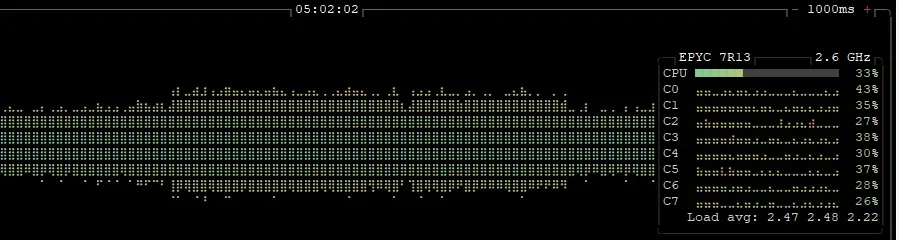
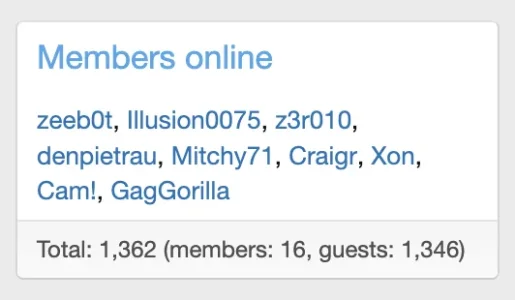
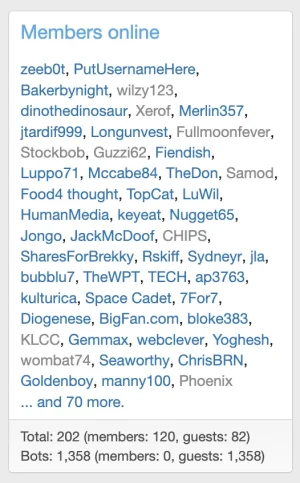
It's interesting you mention this... earlier yesterday, my name servers (DNS) took in a rather notable amount of requests/traffic of A and AAAA records. At first, I thought it was just another reflection attack (they're typical, and RRL's deal with it cleanly), but this go around it was a single datacenter provider known as WebNX, Inc.. This provider's IPv6 range was absolutely slamming my name servers from various/random IPv6 Addresses with what I'd consider blunt-force dictionary/rainbow attacks.We've been running fine since I last posted to this thread but yesterday got hit with a massive attack that resulted in an error 522, and max'd out our resources.
IPv4 you could deal with, but ugh, these huge IPv6 blocks that these providers are being granted are going to lead us back to the IPv4 issue in many decades down the road. I digress... about an hour later, numerous new IP addresses from ranges that were far outside of previous residential proxies and abusive datacenter IP ranges began trying to access port 443 on the successful hits of A/AAAA records.
Didn't knock anything offline in my case. Most of my firewall and filtering configurations nabbed it all before it got out of hand. I could only imagine the result if filtering and WAFs didn't exist... :/