
And the irony, it gives them no real privacy at all. About the only thing a VPN is good for nowadays, is ease of grabbing an IP in another country.people are pushed vpn's all over the place for "security"
Last edited:

And the irony, it gives them no real privacy at all. About the only thing a VPN is good for nowadays, is ease of grabbing an IP in another country.people are pushed vpn's all over the place for "security"
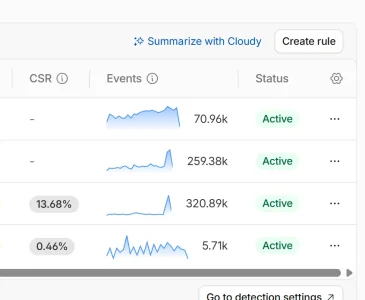

I have been blocking Tencent Cloud and Chinanet for years on the firewall. Zero reason to have any traffic from them. I wish I could block Saleforce too, they are terrible for spam but some legit companies use them.Just took a look at some of the stuff going on right now, that 260k is a block of cf.client.bot and the logs show FB and Tencent / Byteplus (Tiktok), are the problem children. On my managed challenge, China seems to be buying their way through, along with some othe actors.
Wouldn't that be like leaving your house unlocked so you can observe what the thieves like to steal once they are inside your home?Yer... but blocking means you can't see what they're up to. I like to understand what is going on so I can find ways to mitigate it precisely. Yes, you can block China, you can block the ASN, but they have servers worldwide they're using to scrape everything they can get their hands on. I want to understand their techniques to counter them correctly, and that way it doesn't matter what server they use, or from where in the world.

I have China blocked as a country, plus Malaysia and Myanmar, and also ASN's for Tencent and Alibaba etc in other countries, - but why block all those IP's and not the ASN's? Or just block China as a country.I have been blocking Tencent Cloud and Chinanet for years on the firewall. Zero reason to have any traffic from them. I wish I could block Saleforce too, they are terrible for spam but some legit companies use them.
A couple of years ago Saleforce Blacklisted our email server because I was reporting messages as spam. Had to contact the corporate lawyer at Salesforce to get unblocked and they claimed they thought I want to opt out of messages from their network. SMH. Instead of blocking the spammers, they blocked me.
Blocked CHINA Tencent Cloud 42.192.0.0/15, 1.12.0.0/14, 43.136.0.0/16, 111.230.0.0/15, 43.156.0.0/16, 146.56.192.0/18, 43.135.128.0/18, 119.45.0.0/16, 162.14.0.0/16, 129.28.0.0/16, 125.88.0.0/13, 43.138.0.0/15, 175.27.0.0/16, 43.134.64.0/18, 119.28.120.0/22, 119.28.96.0/20, 119.28.112.0/21, 129.226.0.0/16, 43.134.0.0/18, 150.109.0.0/19, 43.163.193.0/24, 43.163.208.0/20, 43.163.192.255, 43.163.96.0/22, 43.163.200.0/21, 43.163.224.0/19, 43.163.194.0/23, 43.153.192.0/18, 43.130.224.0/19, 43.132.96.0/19, 129.226.64.0/20, 43.166.224.0/19, 43.128.128.0/19, 43.160.0.0/12, 43.153.128.0/18, 43.156.35.204, 43.153.0.0/17, 43.155.128.0/17, 121.4.0.0/15, 129.226.160.0/19, 101.32.0.0/18, 101.32.64.0/20, 170.106.0.0/17, 170.106.128.0/19, 170.106.160.0/21, 43.134.224.0/19, 43.154.0.0/16, 43.155.0.0/17, 43.128.64.0/18, 43.133.160.0/19, 124.156.96.0/19, 124.156.128.0/18, 43.157.128.0/18, 139.155.0.0/16, 101.33.64.0/19, 101.33.96.0/22, 43.157.192.0/18, 150.109.224.0/19, 150.109.208.0/20, 43.163.0.0/17, 43.132.128.0/18, 129.226.128.0/20, 129.226.96.0/19, 119.28.0.0/15, 43.133.32.0/19, 124.156.192.0/20, 43.133.96.0/19, 43.134.192.0/19, 43.157.0.0/17, 150.109.144.0/20, 161.120.168.0/22, 43.133.224.0/19, 162.62.208.0/20
Blocked ChinaNet & China Unicom & China Mobile & Cloudie 125.64.0.0/13, 119.120.0.0/13, 112.224.0.0/11, 114.224.0.0/12, 219.136.0.0/15, 219.128.0.0/13, 113.240.0.0/13, 116.224.0.0/12, 183.192.0.0/10, 113.112.0.0/13, 118.112.0.0/13, 182.32.0.0/12, 43.137.0.0/16, 180.152.0.0/13, 14.112.0.0/12, 222.72.0.0/15, 222.64.0.0/13, 118.195.128.0/17, 43.136.0.0/16, 182.128.0.0/12, 111.176.0.0/13, 180.96.0.0/11, 222.92.0.0/14, 183.160.0.0/13, 14.16.0.0/12, 210.16.128.0/18, 49.64.0.0/11, 111.0.0.0/10, 116.16.0.0/12, 120.192.0.0/10, 39.128.0.0/10, 183.0.0.0/10, 223.64.0.0/11, 223.112.0.0/14, 223.116.0.0/15, 223.96.0.0/12, 179.106.168.0/21, 168.194.208.0/22, 132.255.184.0/22, 105.242.0.0/16, 45.167.36.0/22, 191.241.192.0/19, 179.63.236.0/22, 203.130.32.0/19, 14.144.0.0/12, 117.24.0.0/13, 125.40.0.0/13, 101.44.160.0/20, 39.64.0.0/11, 117.50.0.0/16, 43.154.0.0/16, 43.153.128.0/18, 106.224.0.0/12, 182.84.0.0/14, 182.96.55.36, 27.16.0.0/12, 103.115.56.0/22, 103.115.48.0/22, 150.109.96.0/19, 36.227.0.0/16, 211.157.192.0/20, 211.157.128.0/18
Not really. One just wants to take what is already available online, they just don't want to respect whether they cripple your server or not. Anyone creating an account to steal hidden data, yep, that is the same, because now you've locked the door.Wouldn't that be like leaving your house unlocked so you can observe what the thieves like to steal once they are inside your home?
Depends. Given that the US are by far the biggest source of bots (as can be seen on CF radar) and loads of scrapers come from there, residential proxies as well as data-center based ones one might consider this rather unfortunate than fortunate. Definitively makes it more difficult to filter out the scrapers.Fortunately, our community’s audience is primarily focused in the US, Canada, and UK.

Got them, like others here, and they're solving those too. Lots of data analysis.When the observability you're after can be achieved with a nicely contained honeypot,

Another finding, and this is one should come at the surprise of no one: these bot runners are now using Google's Quad8 and Cloudflare's 1x4 public DNS. No longer using their ISP / datacenter provided DNS or locally hosted DNS. So DNS as a method of early-warning is effectively useless now unless you're those public DNS providers, being able to see the true query-source IP.Can confirm - just yesterday I caught a few dozen bots trying to get into my private forum, hitting the same URL simultaneously through two different proxies in completely different parts of the world. Passed all Cloudflare filters for ASN/country, for dubious user-agent values and the captcha for not being authenticated; passed Bot Guard's filters as well.
At the speed this is relentlessly escalating, we might (hopefully) get some traction in two possible scenarios:
Who had something on the note of "fighting for the survival of Internet" among their "where do you see yourself in 5 years" answers 4 years ago?
- new RBLs gathering distributed intel over residential proxies and getting them blacklisted on the internet, maybe getting ISPs to react (not holding my breath on that one)
- as this starts looking more and more like fully automated "hacking" by searching for credentials to abuse (for cryptomining or further botnet expansion) and exploiting vulnerabilities, some nations' security agencies might start to get involved, and these guys would not tread lightly.

Oh no, I'm not referring to external/WWW-based VPNs. I'm talking about routing via private IP space for internal communications, and in many instances via a VPN route. For example, I could be using 10.10.0.1/24 on top of the delegated IPv4 and IPv6 WWW/WAN addressing for all ingest servers, and then those same ingest servers having a route active that directs external client requests over that 10.10.0.1/24 network to an internal server group running on 10.20.0.1/24. Similar to how AWS does it with their Overlay Encapsulation and VPC with RFC1918 configurations. That level 1 list would more or less block those communications on a generic firewall configuration.The only issue I noticed is that it would block Bunny CDN sometimes. That is why the script cross checks the Bunny List- https://api.bunny.net/system/edgeserverlist/plain
As for people using a VPN, VPN is kind of like the 1990s blocking your caller ID, nobody would answer. There is no reason for someone to be on our websites using a VPN, especially for e-commerce or forum registration. Nearly always associated with something nefarious.
Nah, no chance. Even if the AI bubble were to completely 'pop', the infrastructure for these botnets / scrapers using AI-enhancement or AI-backed will still exist, and these sort of issues will persist.Maybe there is hope? According to this the AI bubble has burst in China.
Now a days thankfully, with modernized web server services (sounds silly to write it like that), containerizing web services and locking down their cross-talking capabilities against the other containers/services is a good choice. Especially when deployments are managed via a version control system. Makes the "LOL WE HACKED U!!!!" skiddies quite upset when one can just revert and lock down services while a fix is deployed from upstream. Virtualization of servers has been nice as well... but it seems most folks want to go the route of slapping everything to provisionless-containers these days and not deal with virtualization 'stuff'.I used managed hosting myself a long time ago, and having root access was so freeing, although when I switched over it meant a few sleepless nights, worrying about getting hacked into. (A large forum I took over for was hacked at one point, but that was the early 2000s.)
I eventually got everything so buttoned up (along with killing off many sites that weren't being used) that I don't need to worry about it much. Like having two firewalls--the host has one, as do my servers, so if for some reason my rules ever fail I can fall back on theirs. At the moment I run Elasticsearch and MariaDB each on separate servers, and only access them via the local network at the host--the only IPs open to the public are 1) my own IP address and 2) the IP address of a server at a different host, so I always have a backdoor.


We use essential cookies to make this site work, and optional cookies to enhance your experience.

